We do not know how long to retain project files. What should we do?
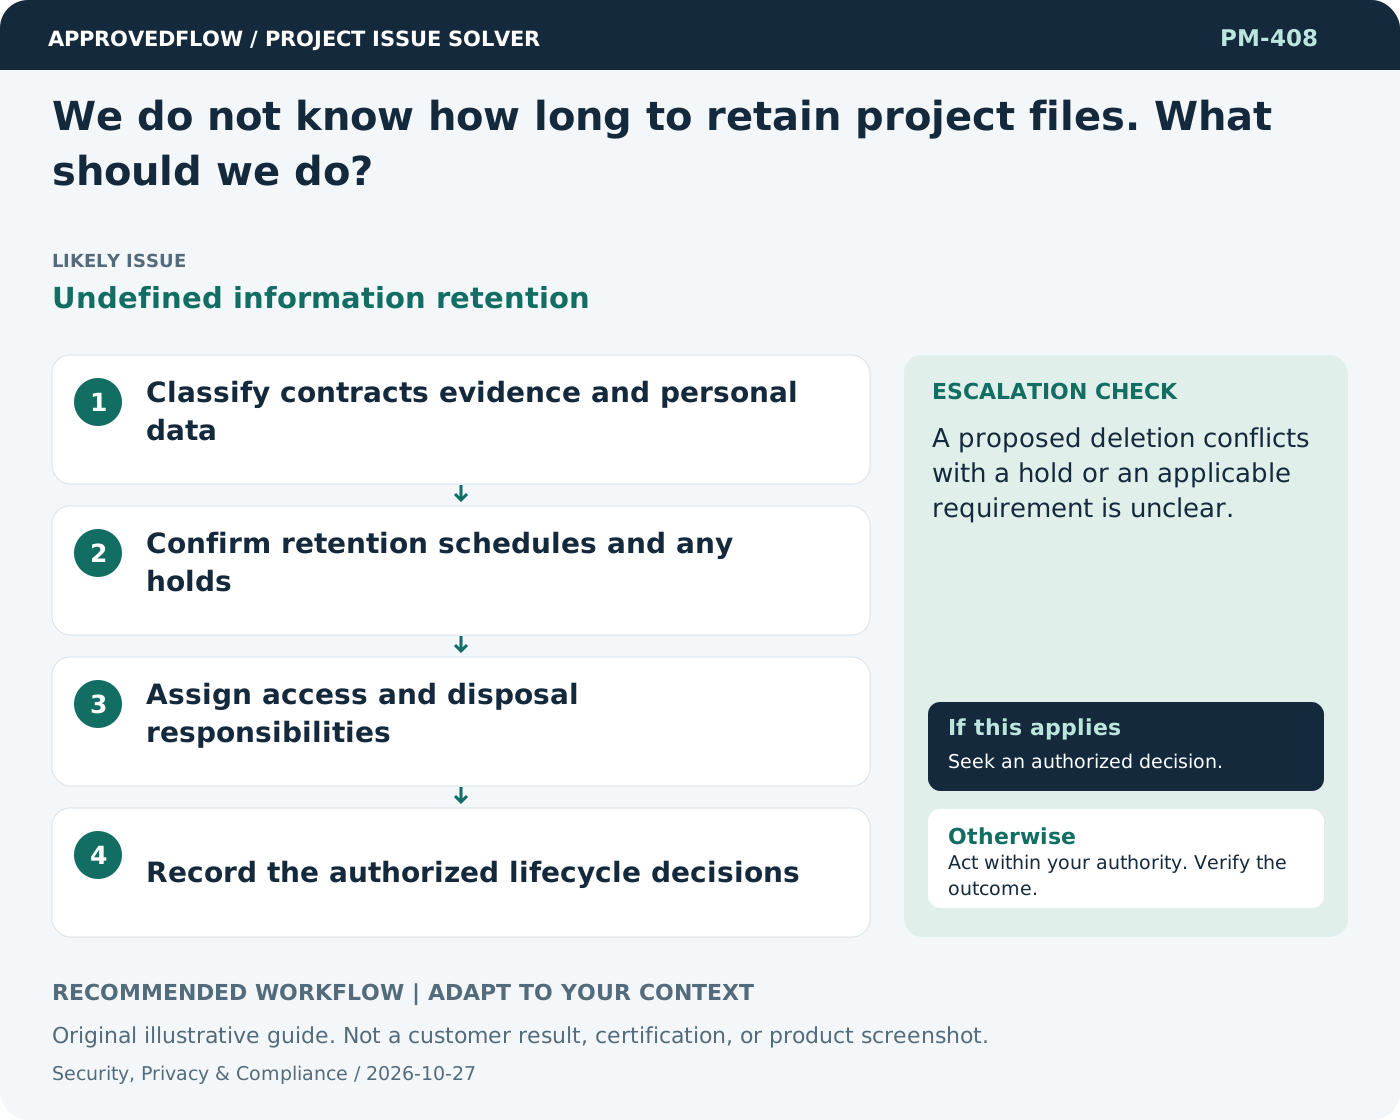
Undefined information retentionAsk the records, legal, and privacy owners to identify the retention rules for each record class. Operational convenience is not a retention policy. Separate approved schedules, legal holds, access restrictions, and disposal responsibilities before deleting or keeping everything indefinitely.
What to do now
- Classify contracts evidence and personal data
- Confirm retention schedules and any holds
- Assign access and disposal responsibilities
- Record the authorized lifecycle decisions
When to escalate
A proposed deletion conflicts with a hold or an applicable requirement is unclear.
The qualified security privacy legal or control owner
Example
Training attendance records and signed contracts receive different approved retention schedules.
Mistake to avoid
Keeping every personal record forever because storage is inexpensive.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Someone pasted a secret key into a project document. What do I do?Potential credential exposure
- Our project manager is asked to sign legal compliance. Should they?Authority and competence mismatch
- How do we know a technical project is ready for handover?Incomplete technical transition
- How do we know whether issue management is improving?Issue metrics without outcomes