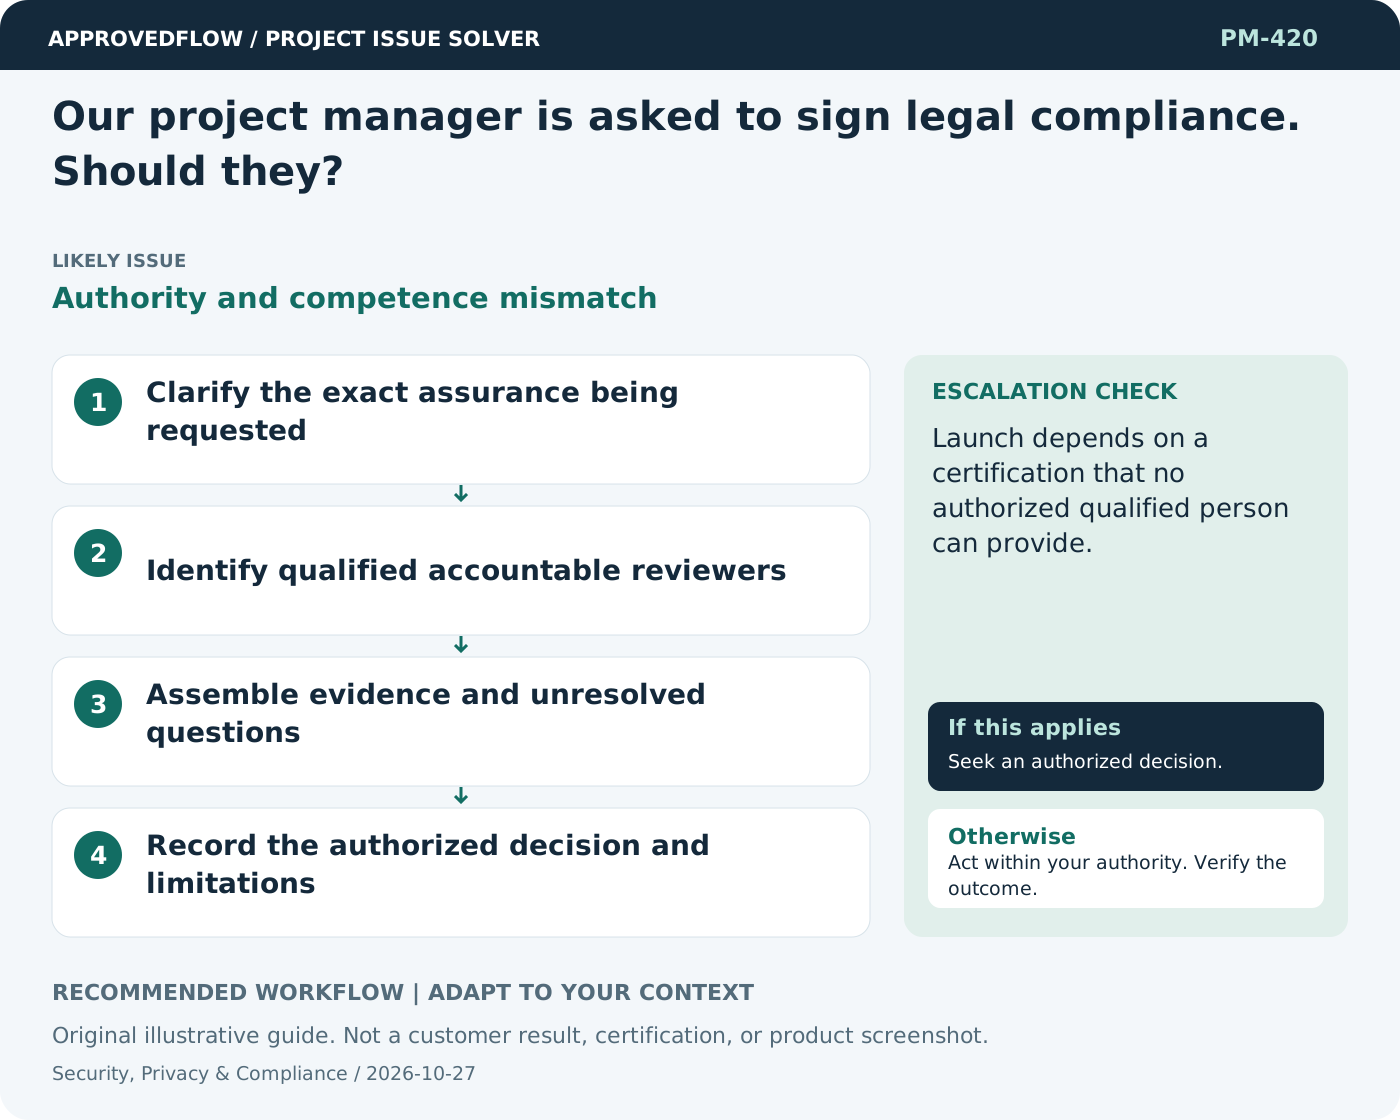
Our project manager is asked to sign legal compliance. Should they?
Authority and competence mismatchA project manager can coordinate compliance work and track evidence, but should not certify matters outside their authority or expertise. Identify the accountable legal, privacy, security, or regulatory owner and obtain a decision based on the relevant requirements and evidence.
What to do now
- Clarify the exact assurance being requested
- Identify qualified accountable reviewers
- Assemble evidence and unresolved questions
- Record the authorized decision and limitations
When to escalate
Launch depends on a certification that no authorized qualified person can provide.
The qualified security privacy legal or control owner
Example
A project manager signs delivery readiness while legal and security owners sign their respective assessments.
Mistake to avoid
Signing a broad compliance statement merely to complete the project checklist.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Our team assumes the hosting country guarantees compliance. Is that enough?Oversimplified data residency assurance
- The supplier says its certificate proves our configuration is secure. Is that true?Assurance scope mismatch
- The customer verbally accepts delivery but will not sign. How should I close?Ambiguous acceptance evidence
- The project manager is asked to approve their own work. Is that sensible?Unclear independent assurance