The project discovered a possible data breach. Should I send details to everyone?
Controlled incident communicationUse your organization's incident reporting channel promptly and let the incident lead coordinate investigation and notifications. Share sensitive details only with authorized responders. Preserve evidence and do not speculate about causes or make external disclosures without the appropriate authority.
What to do now
- Notify the designated incident channel
- Preserve relevant records without altering evidence
- Follow containment instructions from responders
- Coordinate stakeholder updates through the incident lead
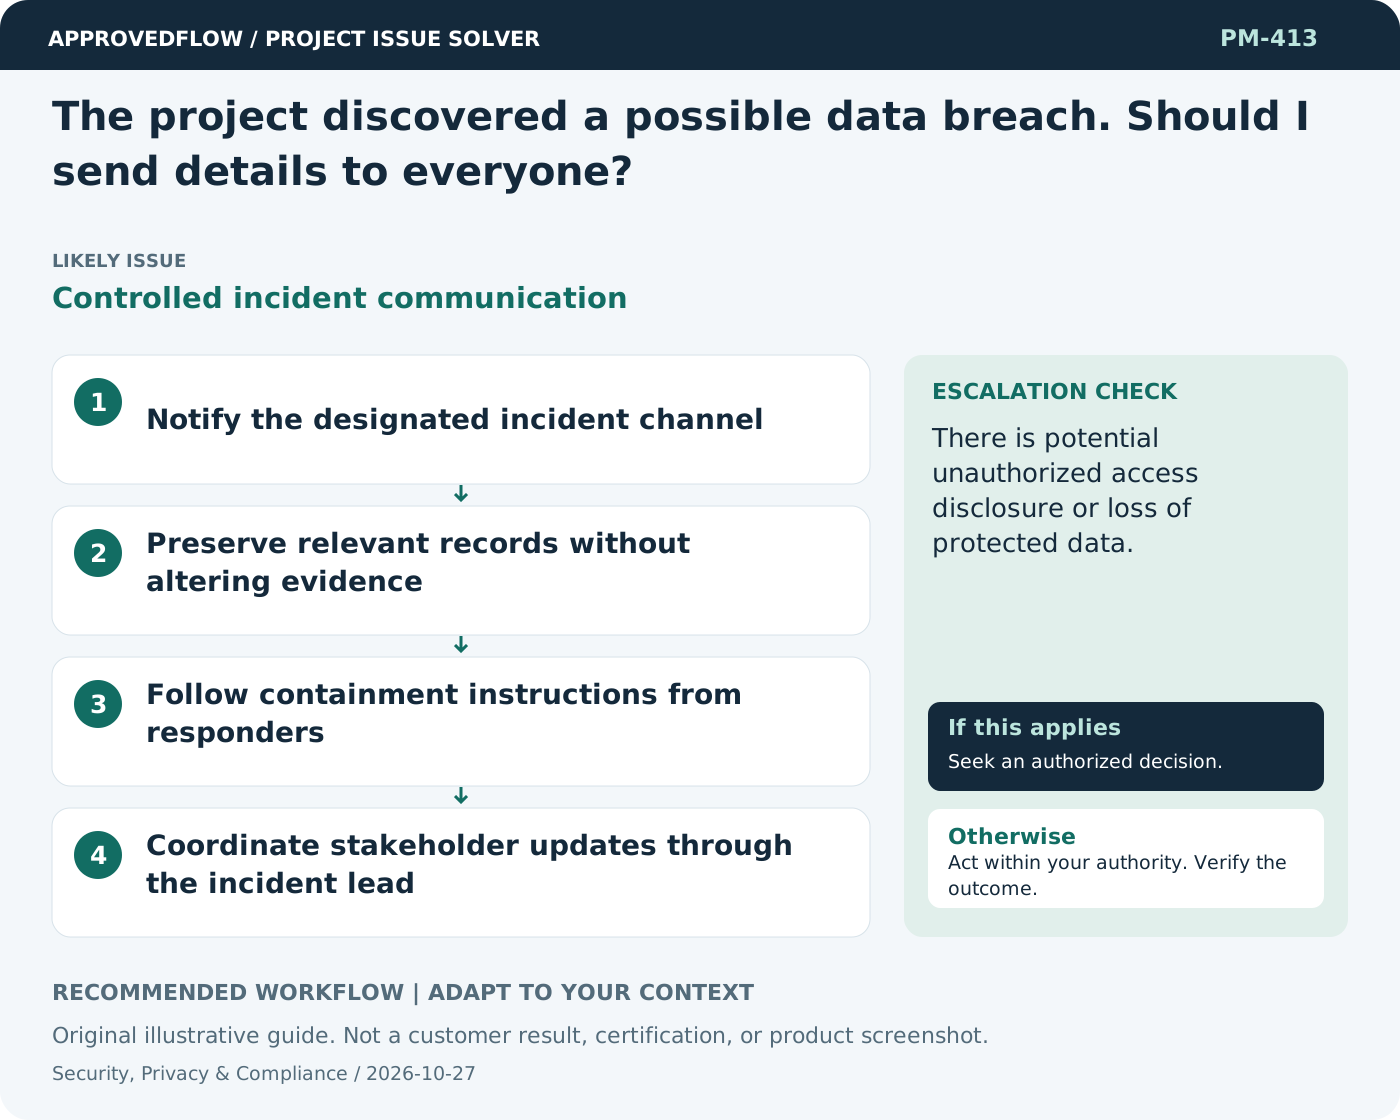
When to escalate
There is potential unauthorized access disclosure or loss of protected data.
The qualified security privacy legal or control owner
Example
The project manager alerts the security lead and sends the sponsor a controlled status update.
Mistake to avoid
Broadcasting screenshots of exposed personal data in a large project group.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Our test environment contains real customer data. Is that acceptable?Uncontrolled test-data exposure
- Our team assumes the hosting country guarantees compliance. Is that enough?Oversimplified data residency assurance
- How do we report a serious issue without alarming everyone?Unclear incident communication
- We discovered a dependency late in the project. How do we assess it?Hidden dependency