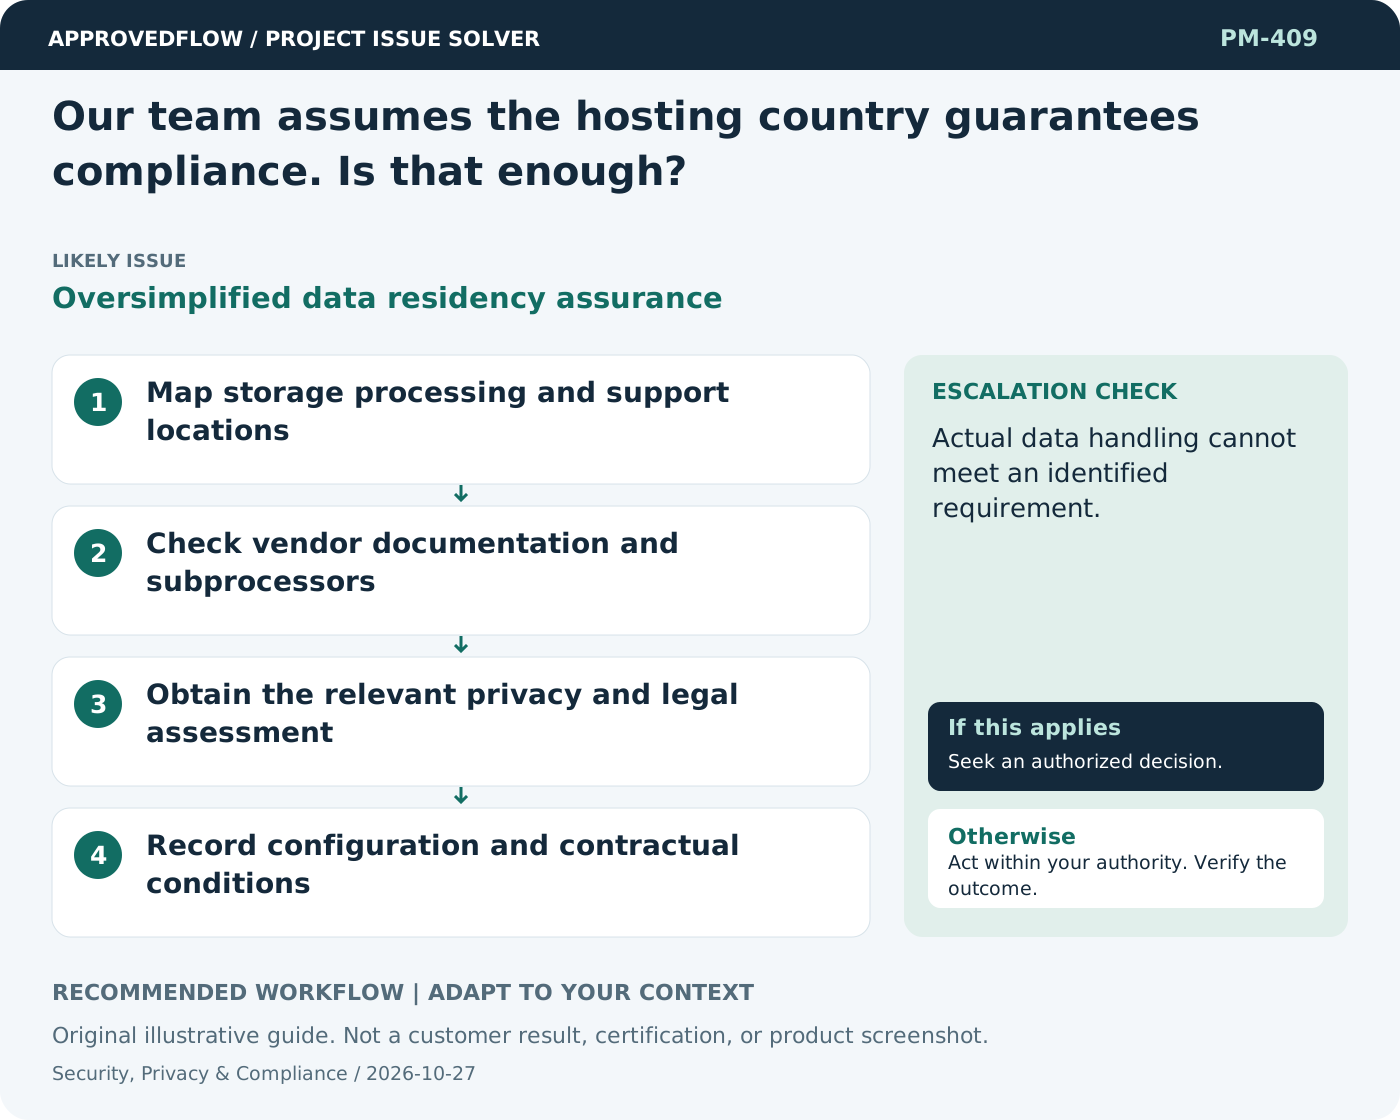
Our team assumes the hosting country guarantees compliance. Is that enough?
Oversimplified data residency assuranceHosting location is only one part of a data-handling assessment. Confirm where processing, backups, support access, and subprocessors operate, and ask qualified privacy or legal owners to assess the applicable obligations. Do not label the project compliant from a region name alone.
What to do now
- Map storage processing and support locations
- Check vendor documentation and subprocessors
- Obtain the relevant privacy and legal assessment
- Record configuration and contractual conditions
When to escalate
Actual data handling cannot meet an identified requirement.
The qualified security privacy legal or control owner
Example
A team discovers that backups and support access need review beyond its selected hosting region.
Mistake to avoid
Advertising compliance solely because a server is in a particular country.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Our project manager is asked to sign legal compliance. Should they?Authority and competence mismatch
- A privacy assessment is requested after requirements are frozen. What now?Late privacy impact assessment
- The supplier provides a certificate but no test evidence. Is that enough?Unverified assurance evidence
- Our business case assumes savings that nobody can explain. Should we accept it?Unsupported benefit assumptions