Our test environment contains real customer data. Is that acceptable?
Uncontrolled test-data exposureDo not assume production data is appropriate for testing. Ask the privacy and security owners to assess the purpose, permissions, safeguards, and applicable requirements. Prefer synthetic or appropriately de-identified data when it can test the same behavior.
What to do now
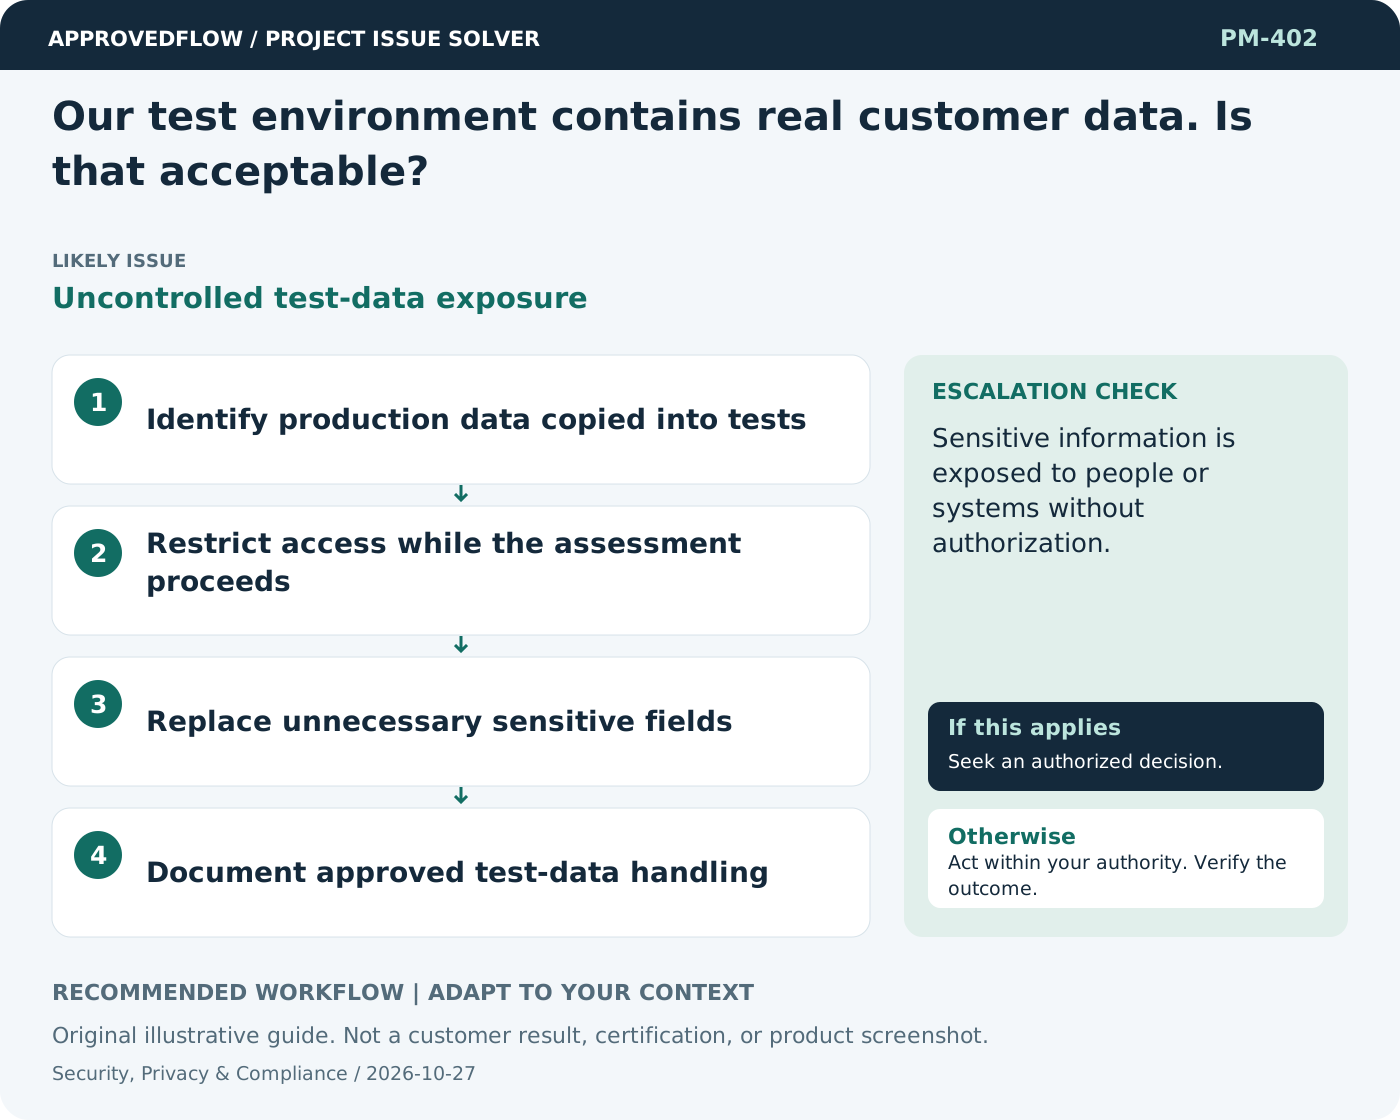
- Identify production data copied into tests
- Restrict access while the assessment proceeds
- Replace unnecessary sensitive fields
- Document approved test-data handling
When to escalate
Sensitive information is exposed to people or systems without authorization.
The qualified security privacy legal or control owner
Example
A migration test uses generated customer records instead of exporting a live contact database.
Mistake to avoid
Assuming that removing names alone makes every dataset anonymous.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Someone pasted a secret key into a project document. What do I do?Potential credential exposure
- Our team assumes the hosting country guarantees compliance. Is that enough?Oversimplified data residency assurance
- The test environment differs from production. How much does that matter?Unrepresentative verification
- The customer signs off a demo but rejects real use. Why?Demonstration-acceptance gap