A security exception is about to expire before delivery. Who decides?
Unmanaged temporary risk acceptanceAn exception should have an owner, scope, compensating controls, and expiry. Obtain an updated assessment before the expiry and seek a decision from the authorized risk owner. Do not extend the exception silently to keep the project schedule unchanged.
What to do now
- Read the original exception conditions
- Check remediation progress and current exposure
- Present remediation or renewal options
- Record the authorized decision and expiry
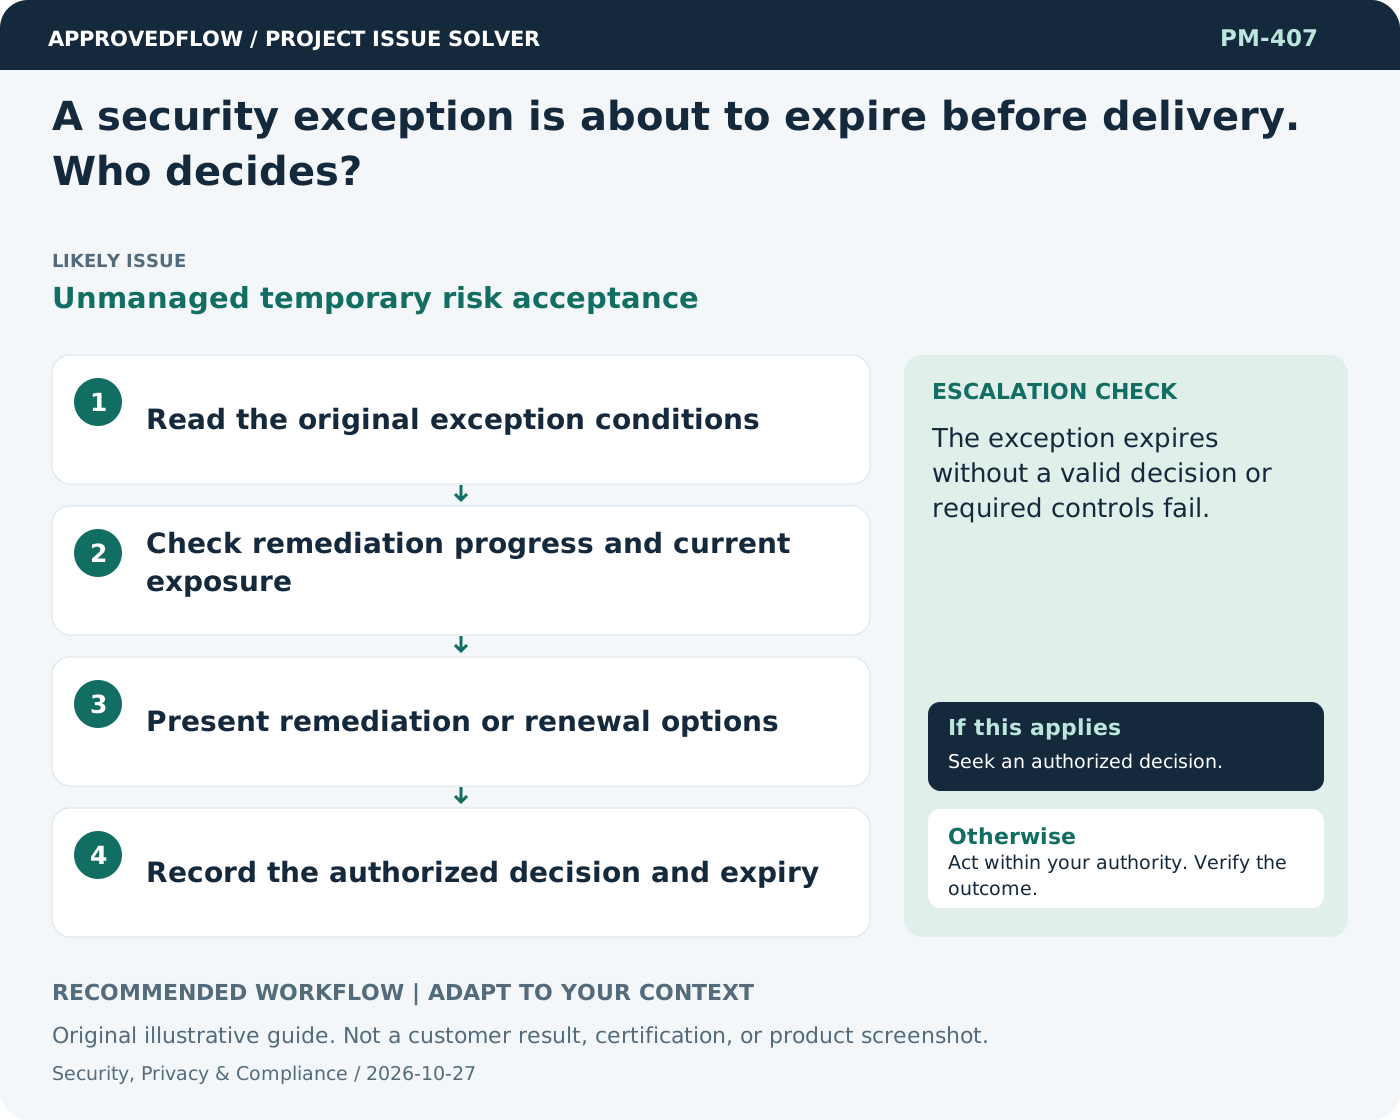
When to escalate
The exception expires without a valid decision or required controls fail.
The qualified security privacy legal or control owner
Example
A temporary network exception is reviewed with a remediation milestone before its access window closes.
Mistake to avoid
Copying the old approval date into a new document.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Security review is scheduled one week before launch. What should I do?Late security assurance
- The supplier says its certificate proves our configuration is secure. Is that true?Assurance scope mismatch
- How do we stop temporary technical shortcuts becoming permanent?Unmanaged technical exceptions
- Our acceptance criteria change after delivery. What should we do?Moving acceptance boundary