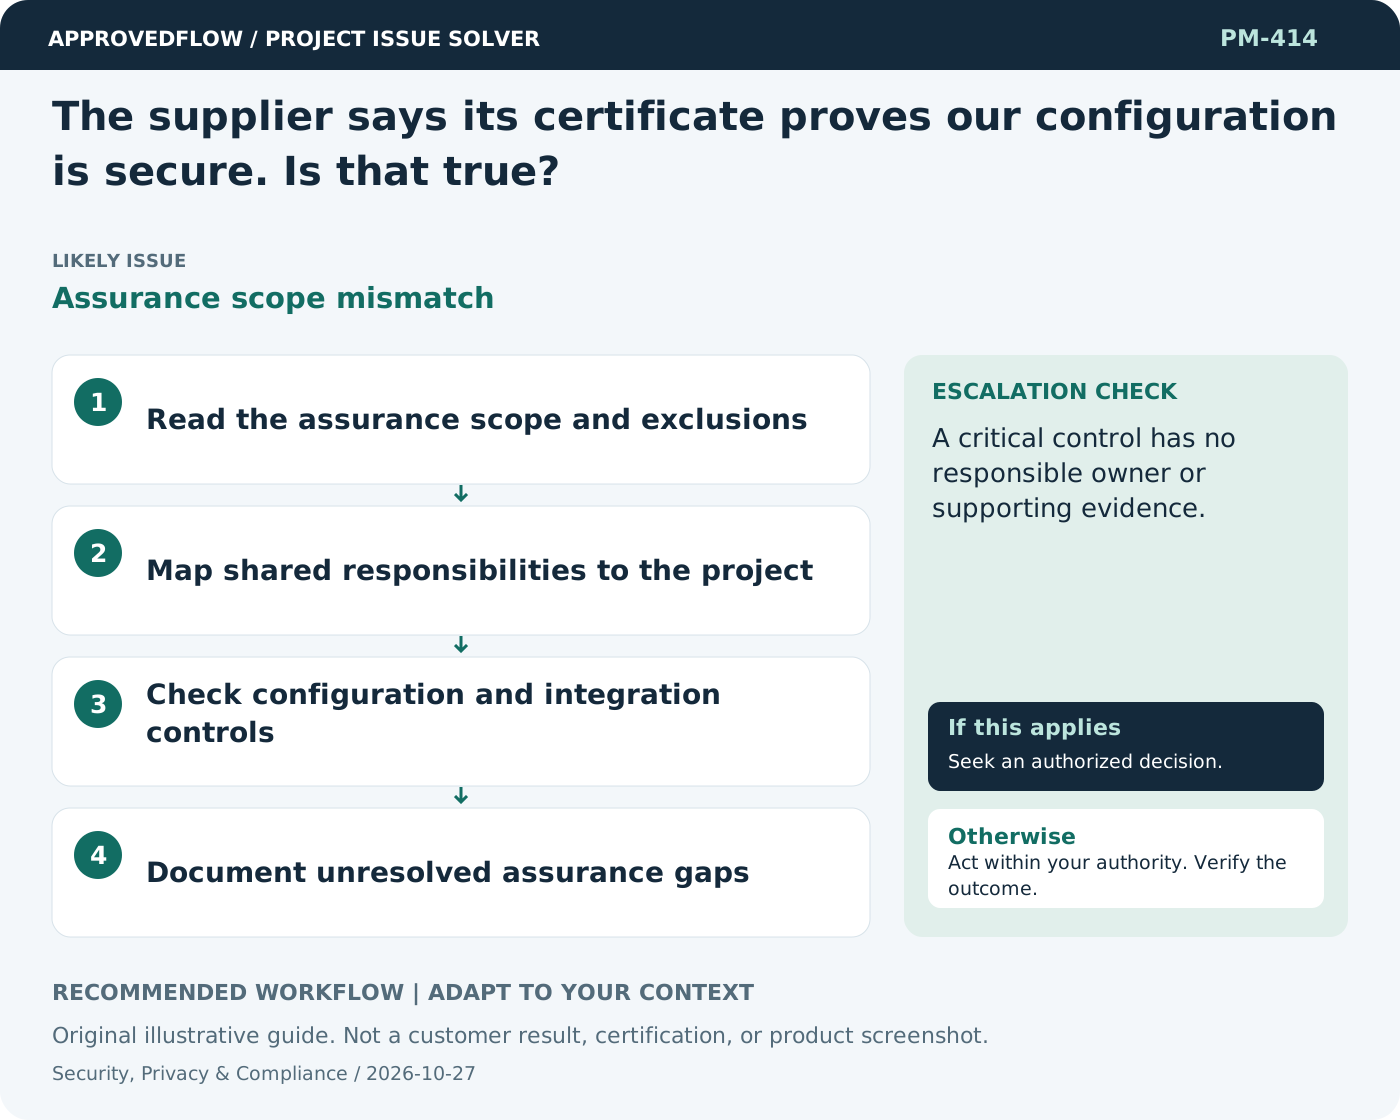
The supplier says its certificate proves our configuration is secure. Is that true?
Assurance scope mismatchA supplier certificate may provide relevant assurance within its stated scope, but it does not establish the security of every configuration or integration. Review the coverage, exclusions, current validity, and your responsibilities, then obtain evidence for project-specific controls.
What to do now
- Read the assurance scope and exclusions
- Map shared responsibilities to the project
- Check configuration and integration controls
- Document unresolved assurance gaps
When to escalate
A critical control has no responsible owner or supporting evidence.
The qualified security privacy legal or control owner
Example
A certified cloud service still requires the customer to configure access and backup controls correctly.
Mistake to avoid
Treating a logo on a proposal as proof of end-to-end security.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Security review is scheduled one week before launch. What should I do?Late security assurance
- A security exception is about to expire before delivery. Who decides?Unmanaged temporary risk acceptance
- The supplier provides a certificate but no test evidence. Is that enough?Unverified assurance evidence
- The vendor says knowledge transfer is not included. How do we respond?Missing supplier transition scope