Security review is scheduled one week before launch. What should I do?
Late security assuranceTreat the late review as a delivery risk, not a formality to rush through. Identify the system's exposure, arrange a qualified review of critical controls, and make launch conditional on resolving or explicitly accepting remaining risks through the proper authority.
What to do now
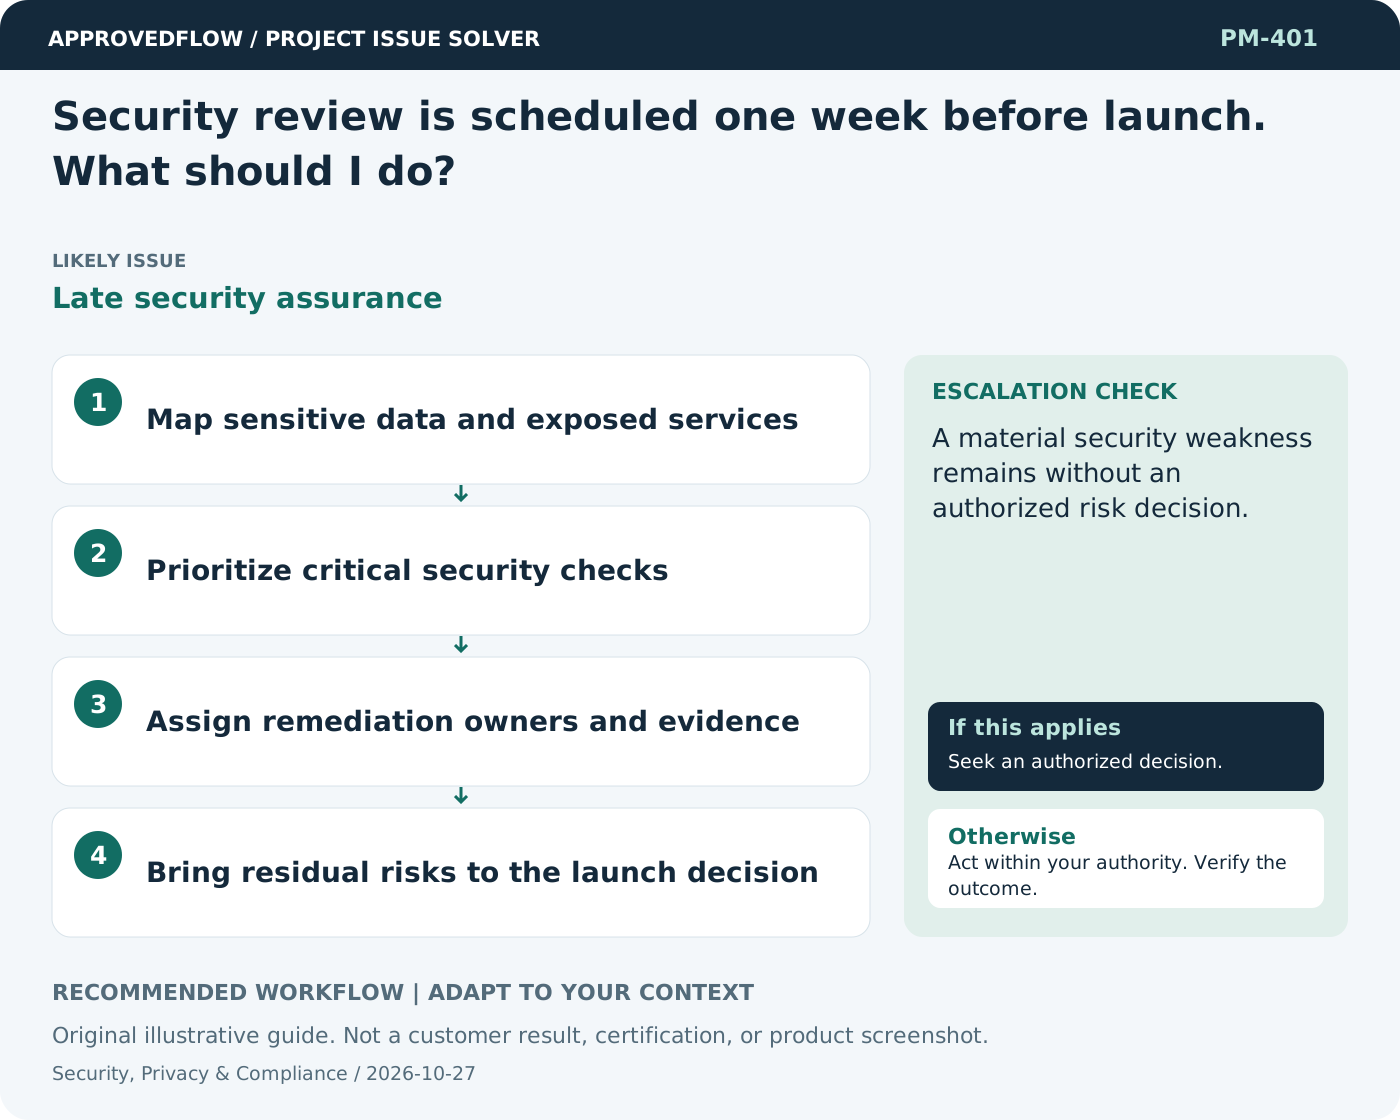
- Map sensitive data and exposed services
- Prioritize critical security checks
- Assign remediation owners and evidence
- Bring residual risks to the launch decision
When to escalate
A material security weakness remains without an authorized risk decision.
The qualified security privacy legal or control owner
Example
A portal launch is reduced to a limited internal pilot while authentication findings are resolved.
Mistake to avoid
Treating a calendar deadline as evidence that a system is safe.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- The supplier says its certificate proves our configuration is secure. Is that true?Assurance scope mismatch
- We have backups, but no one has tested recovery. Can we launch?Unproven recoverability
- Testing is scheduled only at the end. How can we reduce risk now?Late quality feedback
- The project goes live next week, but there is no support model. Can we proceed?Incomplete service transition