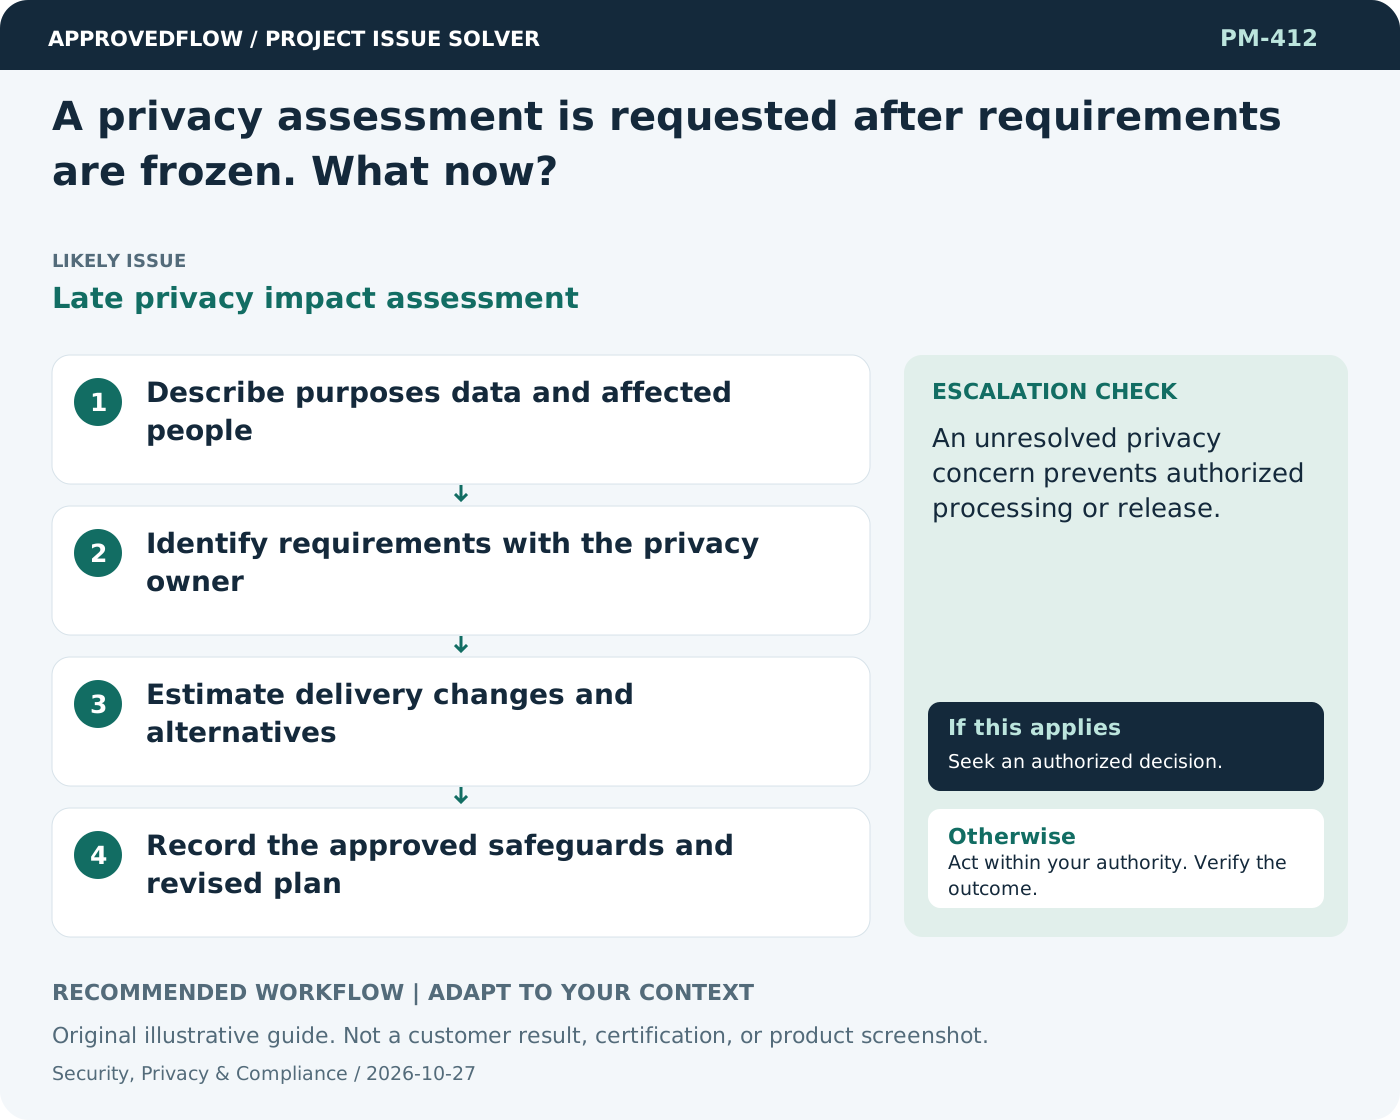
A privacy assessment is requested after requirements are frozen. What now?
Late privacy impact assessmentBring the privacy owner into a focused review of the planned data use. Identify whether requirements, interfaces, consent arrangements, or retention need to change. Use change control for material delivery effects, but do not treat a frozen baseline as permission to ignore necessary safeguards.
What to do now
- Describe purposes data and affected people
- Identify requirements with the privacy owner
- Estimate delivery changes and alternatives
- Record the approved safeguards and revised plan
When to escalate
An unresolved privacy concern prevents authorized processing or release.
The qualified security privacy legal or control owner
Example
A registration form removes unnecessary personal fields after a purpose and retention review.
Mistake to avoid
Calling privacy changes optional simply because design was approved earlier.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- A contractor still has access after leaving the project. What now?Incomplete access offboarding
- Security review is scheduled one week before launch. What should I do?Late security assurance
- The new system changes people's responsibilities, but nobody told them. What now?Unmanaged role transition
- How do we assess the impact of a change properly?Incomplete change analysis