A critical vulnerability appears during the final project week. What should I prioritize?
Release-time vulnerability riskAsk the security owner to assess exploitability, exposure, impact, and available mitigations. Integrate the remediation and verification work into the release decision. A severity label is useful context, but it should not replace an assessment of the actual deployed environment.
What to do now
- Confirm affected components and exposure
- Obtain a qualified risk assessment
- Implement and verify an approved remediation
- Record the release or deferral decision
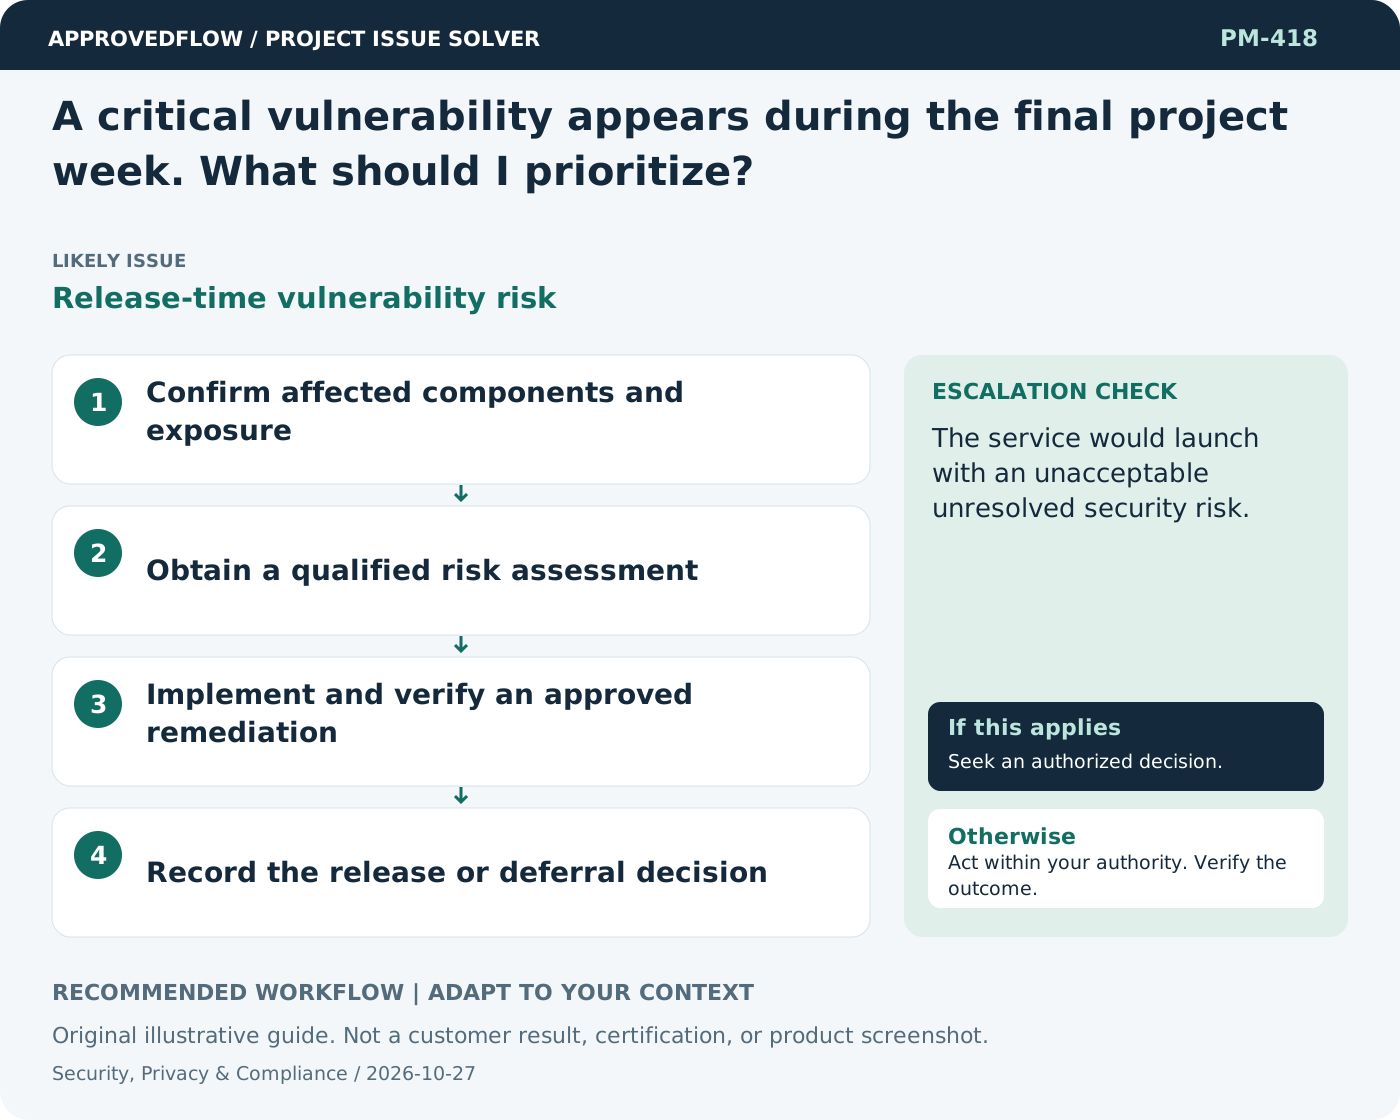
When to escalate
The service would launch with an unacceptable unresolved security risk.
The qualified security privacy legal or control owner
Example
A vulnerable component is patched and regression-tested before the affected public endpoint is enabled.
Mistake to avoid
Hiding the finding in a future backlog to preserve the milestone.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Security review is scheduled one week before launch. What should I do?Late security assurance
- The team shares one administrator account. How do we change this?Weak individual accountability
- How do we prevent interface changes during final testing?Interface stabilization gap
- The team rates every risk as high. How can we prioritize?Undifferentiated risk assessment