The team shares one administrator account. How do we change this?
Weak individual accountabilityShared administrator access makes individual actions difficult to attribute. Work with the system owner to introduce named privileged access and an approved emergency-access procedure, while avoiding a disruptive change that locks the service team out.
What to do now
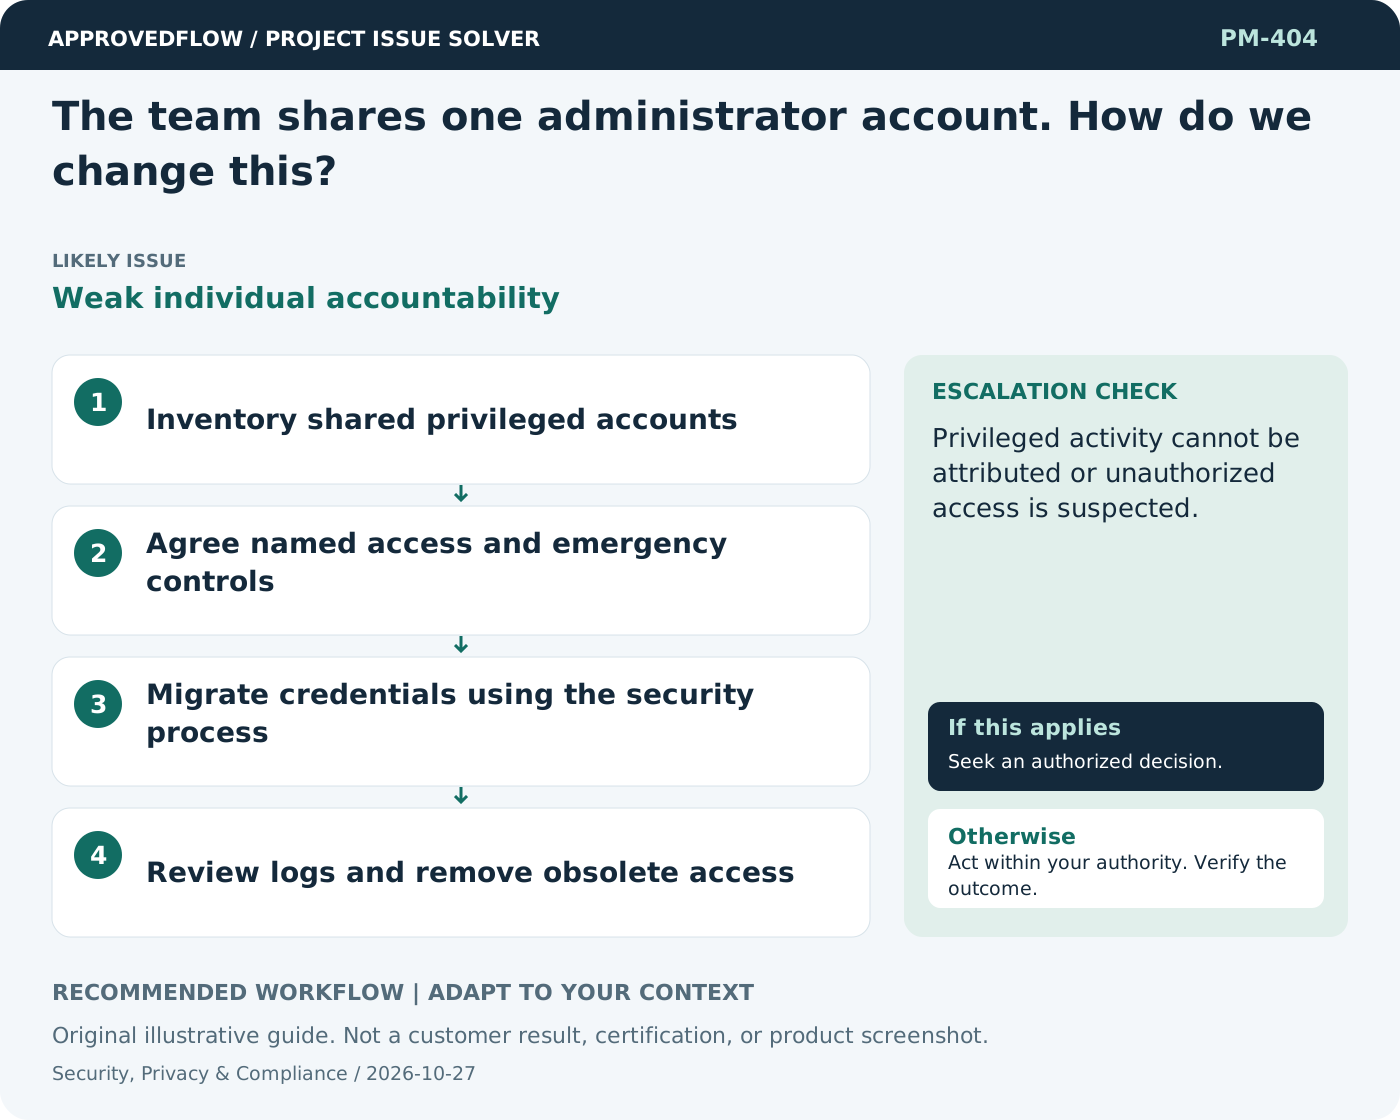
- Inventory shared privileged accounts
- Agree named access and emergency controls
- Migrate credentials using the security process
- Review logs and remove obsolete access
When to escalate
Privileged activity cannot be attributed or unauthorized access is suspected.
The qualified security privacy legal or control owner
Example
A deployment team receives named privileged accounts while an audited emergency account is retained.
Mistake to avoid
Posting a replacement administrator password in the project chat.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Security review is scheduled one week before launch. What should I do?Late security assurance
- We have backups, but no one has tested recovery. Can we launch?Unproven recoverability
- Our risk estimates are guesses. Can they still be useful?Weak risk evidence
- No one will accept the service owner role. What should I escalate?Unassigned operational accountability