Developers keep adding new libraries. What should we control?
Unmanaged software dependenciesReview new dependencies for purpose, maintenance, licensing, security, and operating impact with the appropriate owners. Avoid both uncontrolled additions and blanket bans that ignore genuine value.
What to do now
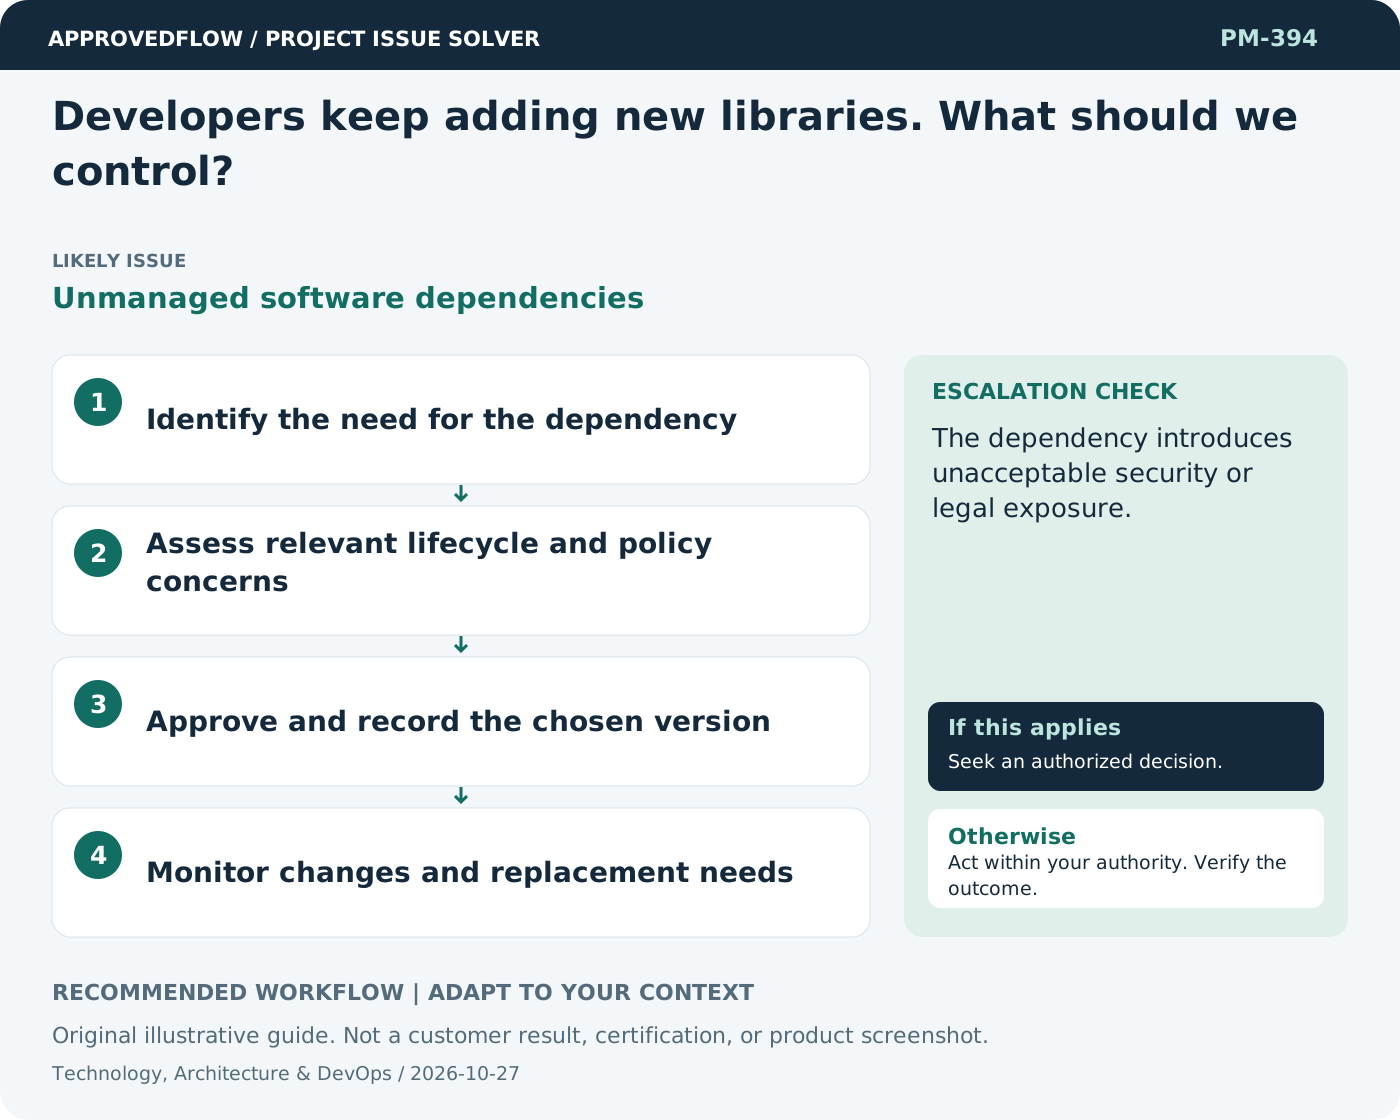
- Identify the need for the dependency
- Assess relevant lifecycle and policy concerns
- Approve and record the chosen version
- Monitor changes and replacement needs
When to escalate
The dependency introduces unacceptable security or legal exposure.
The technical owner and authorized release decision maker
Example
A library is reviewed for its actual required capability and maintenance implications before adoption.
Mistake to avoid
Assuming popularity guarantees suitability or safe licensing.
Prevent a repeat
Review real execution evidence and maintainability alongside feature completion; do not treat an unrun test as passed.
Suggested ApprovedFlow setup
- Tasks
- Documents
- Approvals
Track delivery tasks and attach engineering evidence; keep source control, build execution and technical controls in their actual engineering systems. See the platform
Related cases
- Technical debt keeps delaying new features. How should we prioritize it?Unmanaged technical drag
- We discover integration problems only before release. How can we improve?Late integration feedback
- How do we keep change control lightweight for a small team?Proportionate change recording
- Our project depends on an external approval date we cannot control. What should we do?External decision uncertainty