The security checklist is complete, but permission tests were never run. Is that enough?
Unverified authorization controlsA completed checklist is not evidence that access restrictions work. Test representative roles and forbidden actions in an authorized environment, including cross-project and cross-organization boundaries. Keep evidence of expected denials as well as successful permitted actions.
What to do now
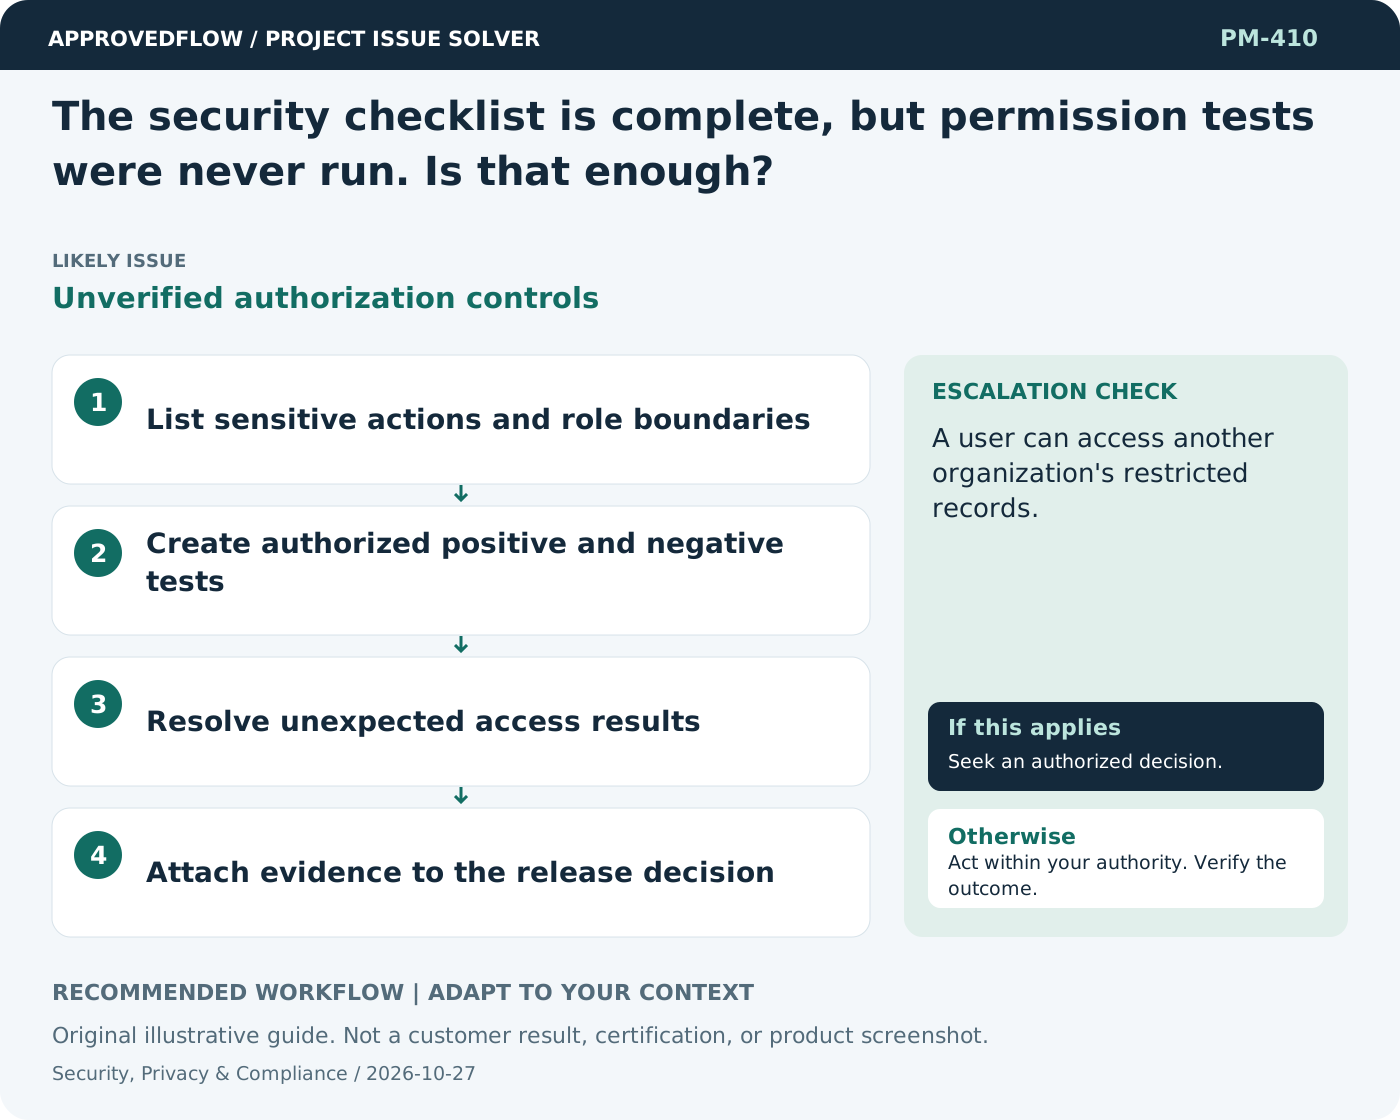
- List sensitive actions and role boundaries
- Create authorized positive and negative tests
- Resolve unexpected access results
- Attach evidence to the release decision
When to escalate
A user can access another organization's restricted records.
The qualified security privacy legal or control owner
Example
A reviewer can approve assigned documents but a negative test verifies they cannot approve unrelated projects.
Mistake to avoid
Testing only whether an administrator can open every page.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Users keep gaining extra roles as the project evolves. What is the risk?Permission accumulation
- Security review is scheduled one week before launch. What should I do?Late security assurance
- A key stakeholder says they were never consulted. How should I respond?Stakeholder engagement gap
- The team built features that were never requested. What should happen?Gold plating