Audit asks for evidence, but the team only has verbal assurances. What can we provide?
Insufficient control evidenceProvide truthful records of what was actually performed, distinguishing documented evidence from recollection. Ask the control owner which missing checks can be performed now and recorded accurately. Never backdate an approval or fabricate evidence to make the audit pack look complete.
What to do now
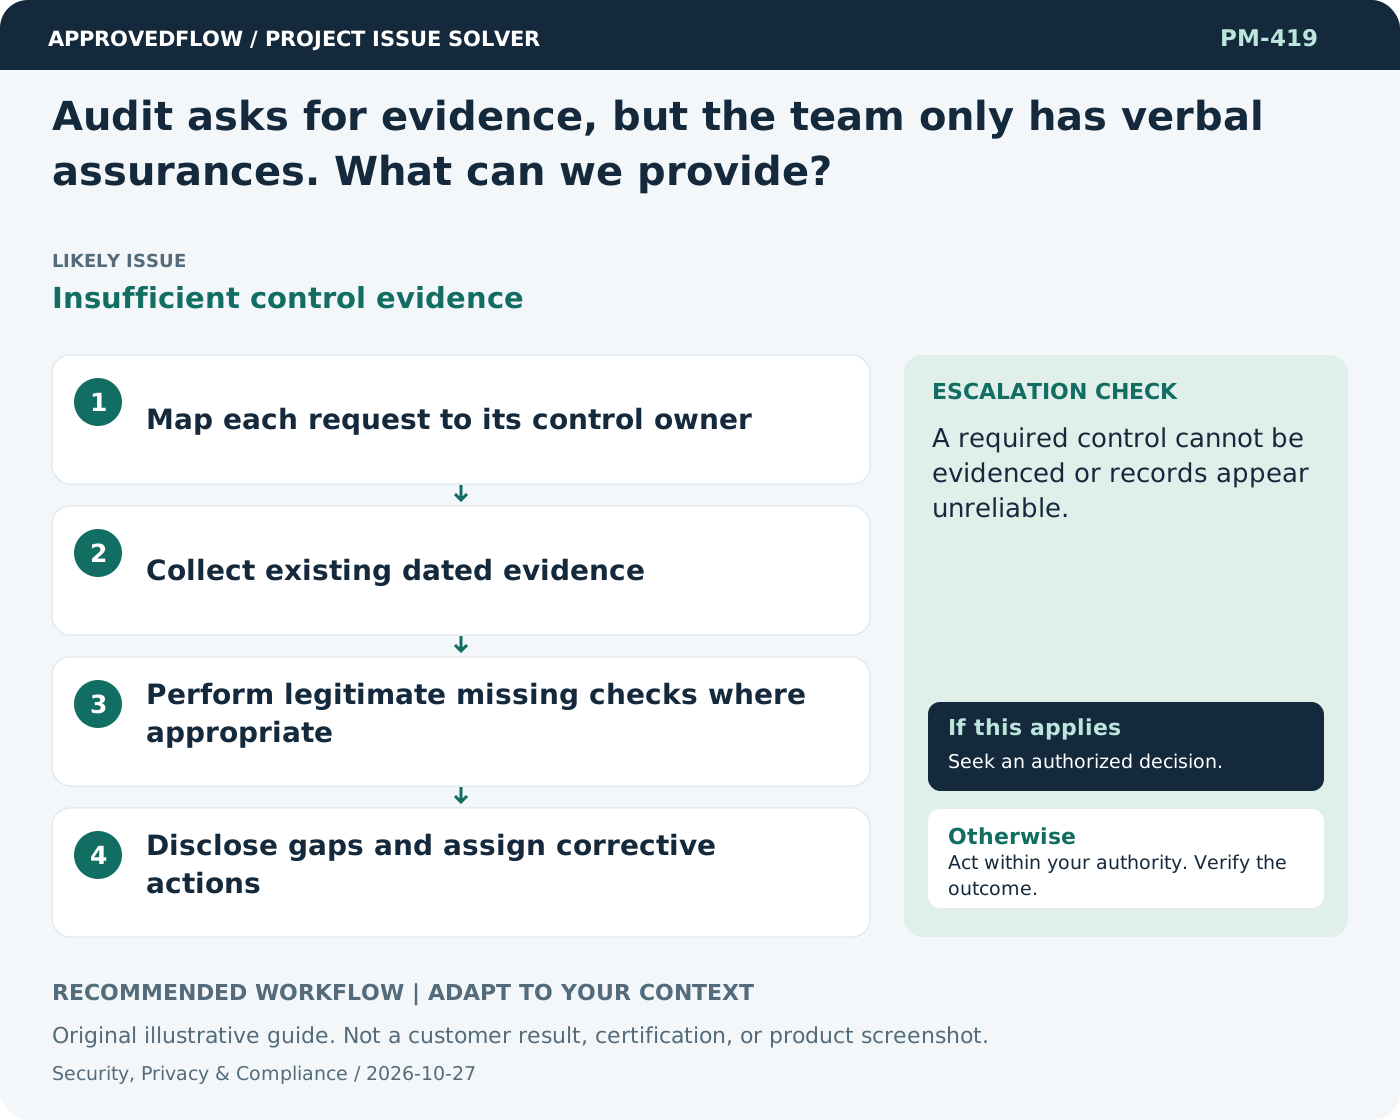
- Map each request to its control owner
- Collect existing dated evidence
- Perform legitimate missing checks where appropriate
- Disclose gaps and assign corrective actions
When to escalate
A required control cannot be evidenced or records appear unreliable.
The qualified security privacy legal or control owner
Example
The team records a current access test and openly notes that the earlier review was undocumented.
Mistake to avoid
Creating a retrospective signature that pretends a review happened earlier.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Our project manager is asked to sign legal compliance. Should they?Authority and competence mismatch
- A critical vulnerability appears during the final project week. What should I prioritize?Release-time vulnerability risk
- We cannot reproduce a reported defect. Should we close it?Insufficient defect evidence
- A decision was made verbally and is now disputed. What should we do?Missing decision evidence