Nobody owns the periodic access review. How do I establish it?
Missing access recertification ownershipAssign a business owner to confirm who still needs access, supported by the identity team. Review actual privileges and external users against current responsibilities, then track removals to completion. A list of accounts without an accountable reviewer is not a control.
What to do now
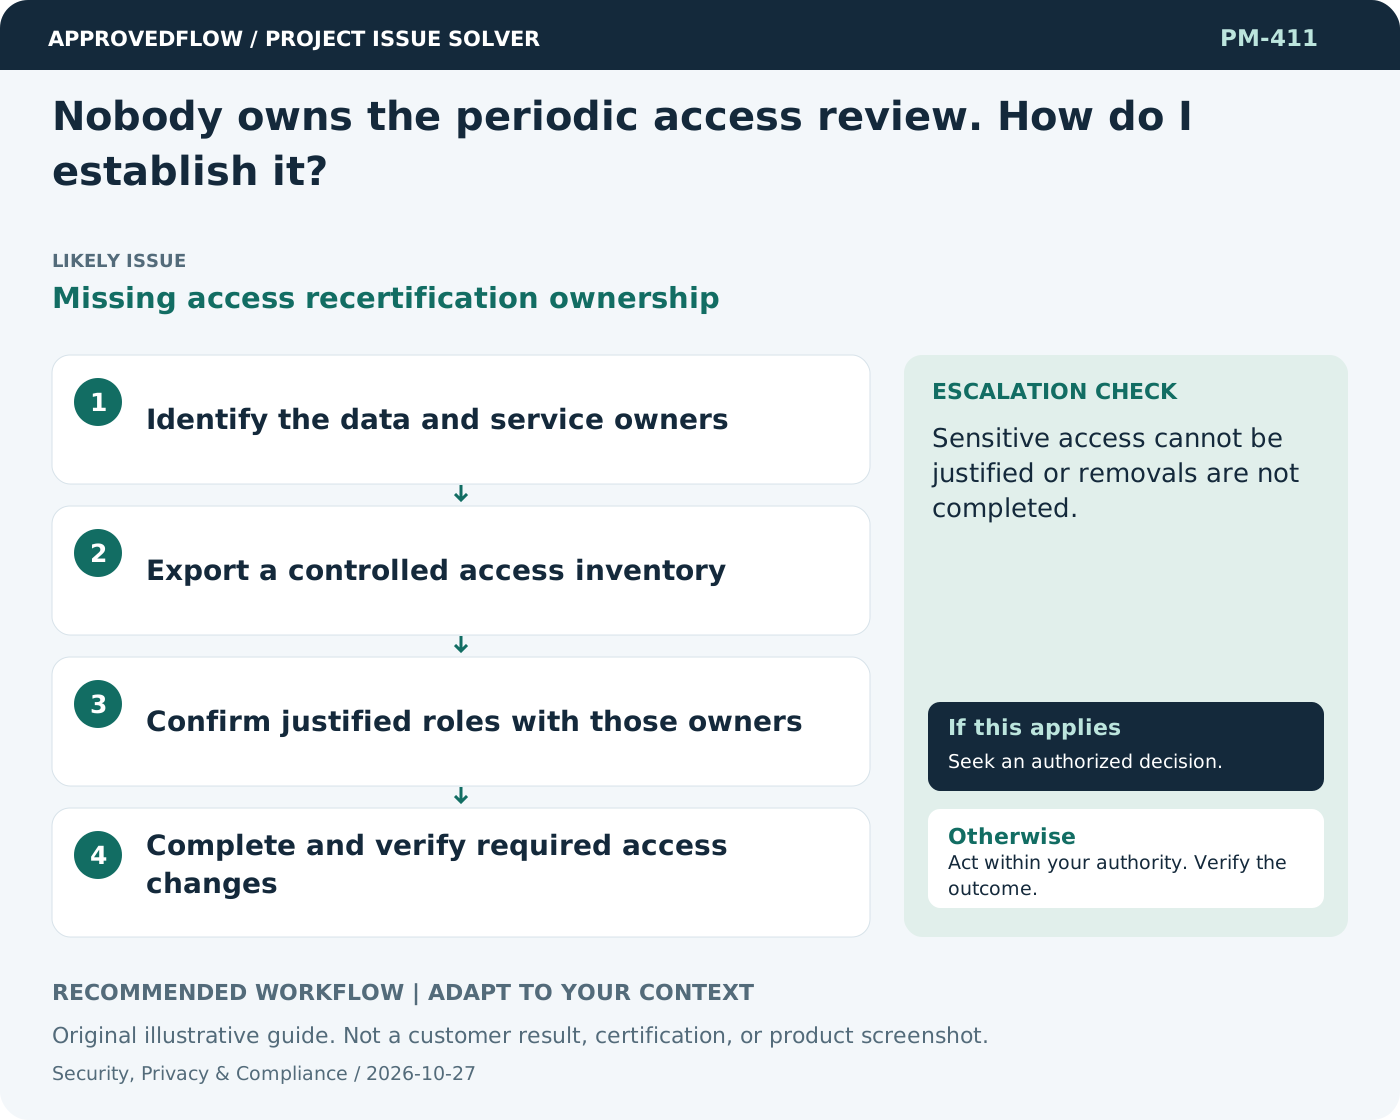
- Identify the data and service owners
- Export a controlled access inventory
- Confirm justified roles with those owners
- Complete and verify required access changes
When to escalate
Sensitive access cannot be justified or removals are not completed.
The qualified security privacy legal or control owner
Example
A quarterly review identifies consultants whose project role ended although their account remains active.
Mistake to avoid
Asking users to approve their own privileged permissions without oversight.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- A contractor still has access after leaving the project. What now?Incomplete access offboarding
- The vendor requests permanent full access for troubleshooting. Should we agree?Excessive support privileges
- Who owns integration in a hybrid program?Missing end-to-end accountability
- The project ends before its benefits can be measured. Who owns the result?Missing post-project benefits ownership