Our consent screen does not match what analytics collects. What should happen?
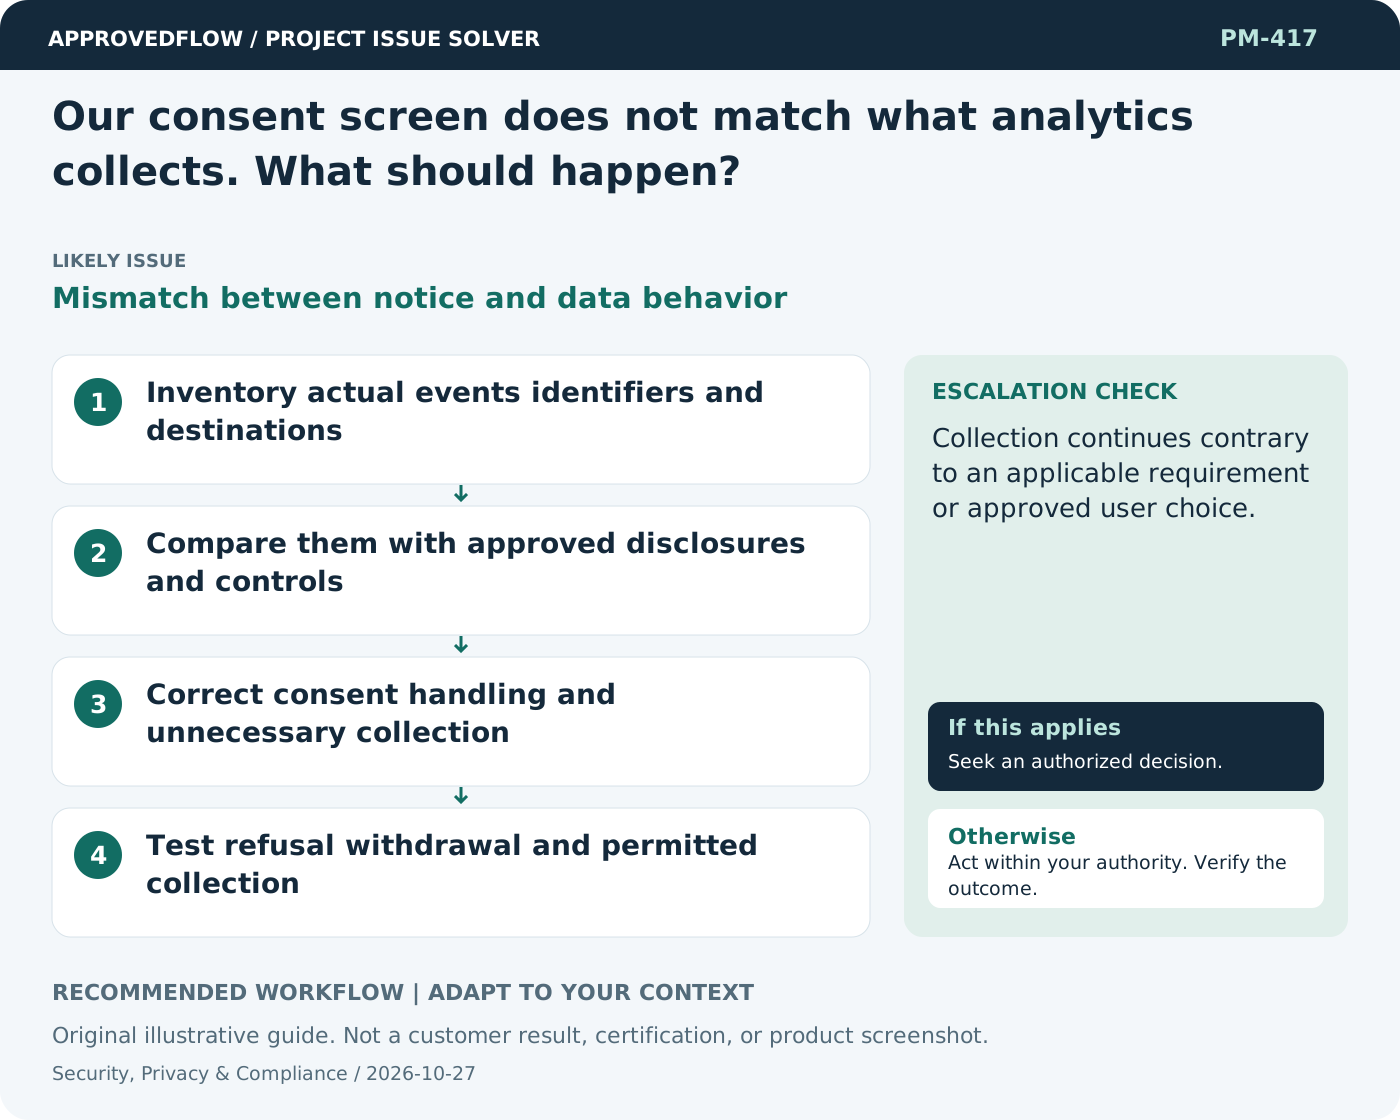
Mismatch between notice and data behaviorHave the privacy and implementation owners compare the actual collection behavior with the approved notice and consent requirements. Correct the mismatch before relying on the consent record. Test both acceptance and refusal paths rather than checking only the screen wording.
What to do now
- Inventory actual events identifiers and destinations
- Compare them with approved disclosures and controls
- Correct consent handling and unnecessary collection
- Test refusal withdrawal and permitted collection
When to escalate
Collection continues contrary to an applicable requirement or approved user choice.
The qualified security privacy legal or control owner
Example
A site test finds an analytics event firing before the visitor has made the required choice.
Mistake to avoid
Assuming a visible banner proves that tracking respects consent.
Prevent a repeat
Review access and controls when scope changes; obtain qualified advice for legal, regulatory and high-impact security decisions.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Track remediation tasks and non-sensitive review evidence; restrict sensitive incident or security detail through the authorized systems and permissions. See the platform
Related cases
- Our test environment contains real customer data. Is that acceptable?Uncontrolled test-data exposure
- Our team assumes the hosting country guarantees compliance. Is that enough?Oversimplified data residency assurance
- A shared API changes without notice. What should happen?Uncontrolled interface change
- How do we schedule integration between teams with different iteration lengths?Cadence integration mismatch