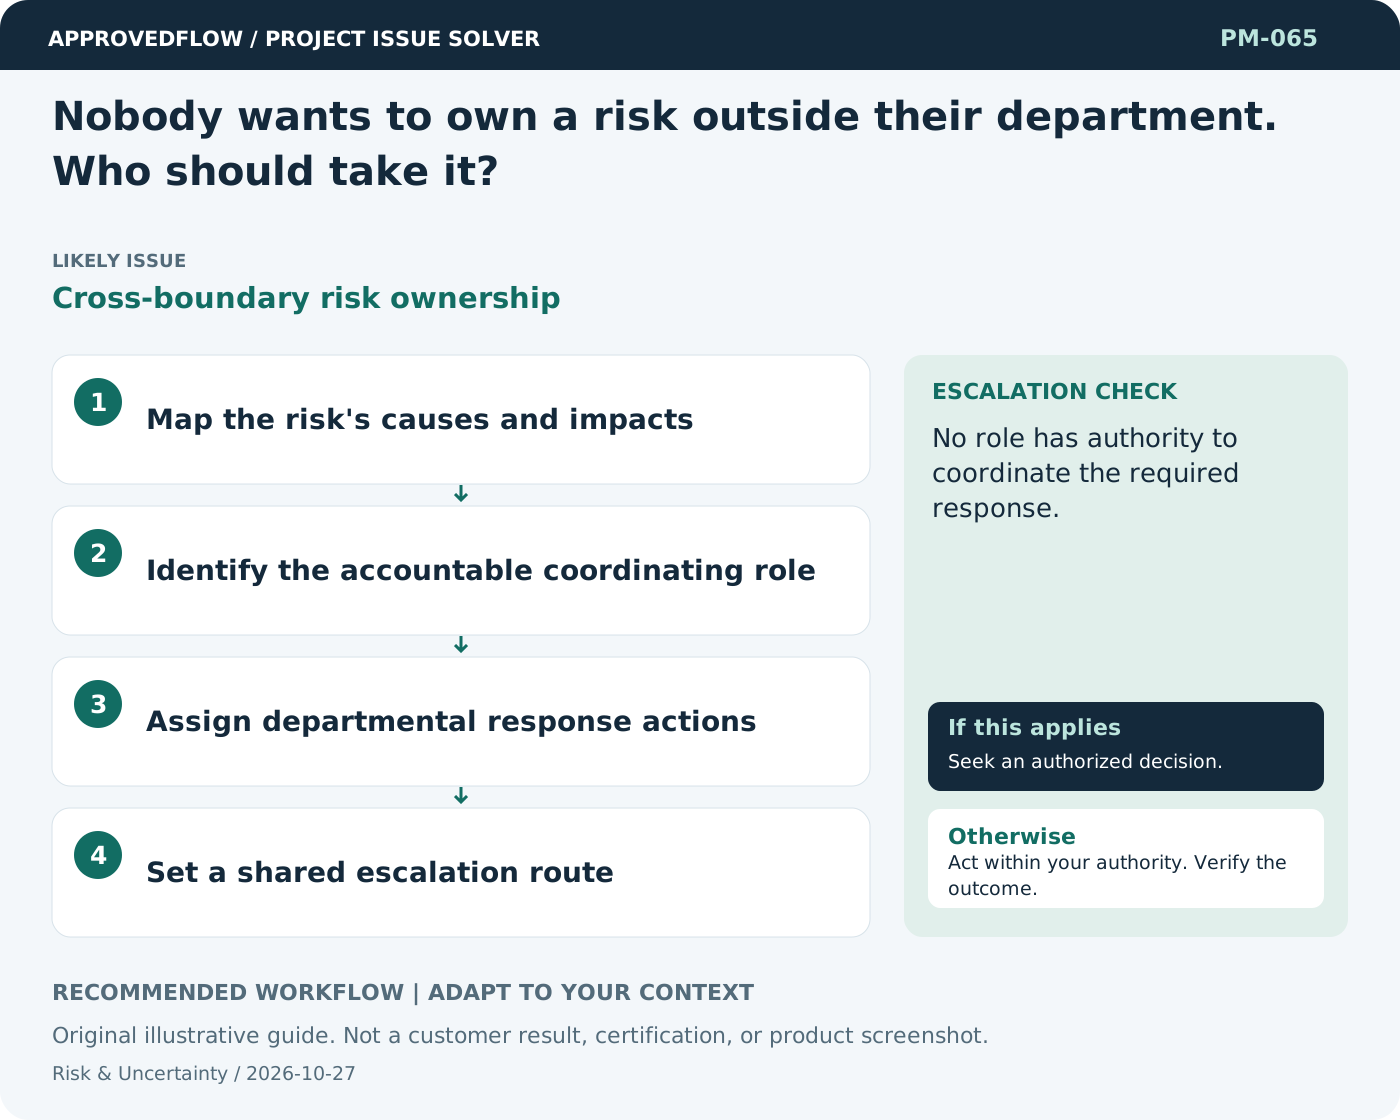
Nobody wants to own a risk outside their department. Who should take it?
Cross-boundary risk ownershipAssign an accountable owner with enough influence to coordinate the response, while naming action owners in each department. Ownership does not mean one person controls every cause.
What to do now
- Map the risk's causes and impacts
- Identify the accountable coordinating role
- Assign departmental response actions
- Set a shared escalation route
When to escalate
Escalate when
No role has authority to coordinate the required response.
Who decides
The accountable risk owner
Example
A data-sharing risk has one coordinating owner and separate legal, security, and operational actions.
Mistake to avoid
Assigning the risk to the project manager by default.
Prevent a repeat
Review whether response tasks and trigger conditions remain appropriate as the project changes.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Store the risk assessment as a controlled project document and assign response tasks; do not assume a native risk engine is enabled. See the platform
Related cases
- Our risk register is long, but nobody acts on it. How do we fix that?Risk log without ownership
- A risk owner left the organization. What should happen immediately?Orphaned risk responsibility
- The change request has no owner after approval. Who is responsible?Unassigned change implementation
- Nobody owns the periodic access review. How do I establish it?Missing access recertification ownership