How often should we review project risks?
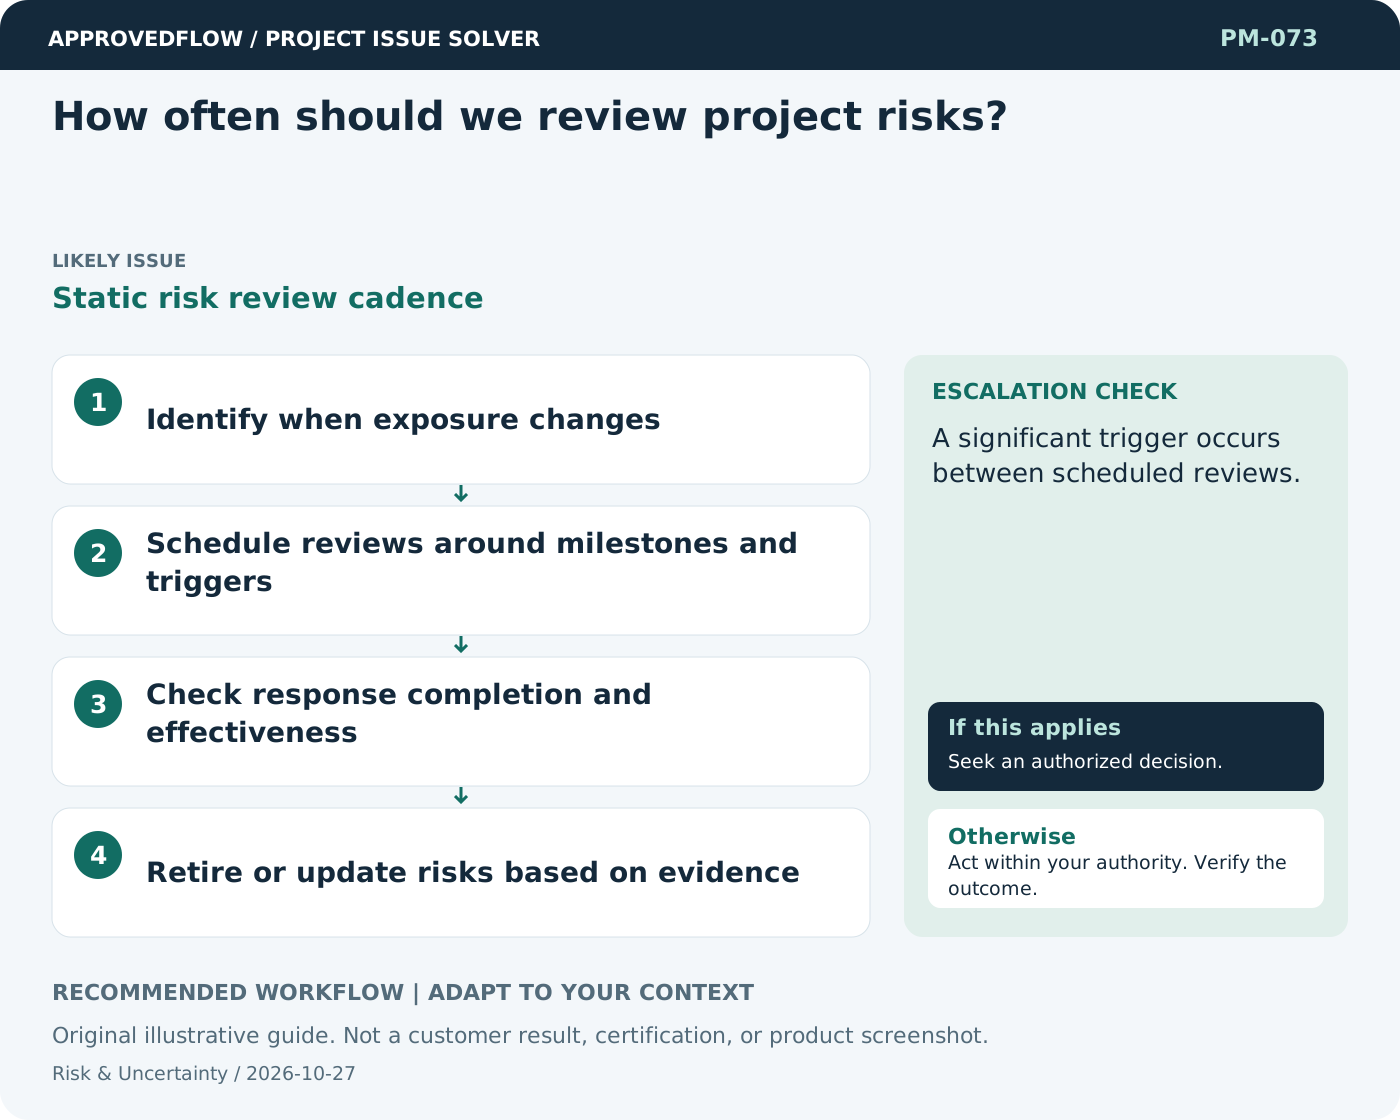
Static risk review cadenceMatch review frequency to the pace of change and the proximity of exposure. Review critical risks at relevant decision points rather than relying only on a fixed monthly meeting.
What to do now
- Identify when exposure changes
- Schedule reviews around milestones and triggers
- Check response completion and effectiveness
- Retire or update risks based on evidence
When to escalate
Escalate when
A significant trigger occurs between scheduled reviews.
Who decides
The accountable risk owner
Example
A stable procurement risk is reviewed monthly, then weekly as the delivery window approaches.
Mistake to avoid
Reusing the same risk register without checking whether conditions changed.
Prevent a repeat
Review whether response tasks and trigger conditions remain appropriate as the project changes.
Suggested ApprovedFlow setup
- Documents
- Tasks
- Approvals
Store the risk assessment as a controlled project document and assign response tasks; do not assume a native risk engine is enabled. See the platform
Related cases
- How do we close a risk properly?Unsupported risk closure
- A low-probability risk could be catastrophic. How do we assess it?Severe low-frequency exposure
- We are closing with residual risks. What must be transferred?Unowned residual risk exposure
- How do we schedule integration between teams with different iteration lengths?Cadence integration mismatch