A colleague pasted confidential project documents into an unapproved AI service. What now?
Unapproved information disclosureFollow your organization's security and privacy reporting process and avoid further uploads. Identify the data involved and the service used so authorized responders can assess exposure and contractual options. Do not assume deleting a chat removes every retained copy.
What to do now
- Stop further sharing through the unapproved route
- Notify the designated security or privacy owner
- Record what was shared and with which service
- Follow the approved assessment and containment process
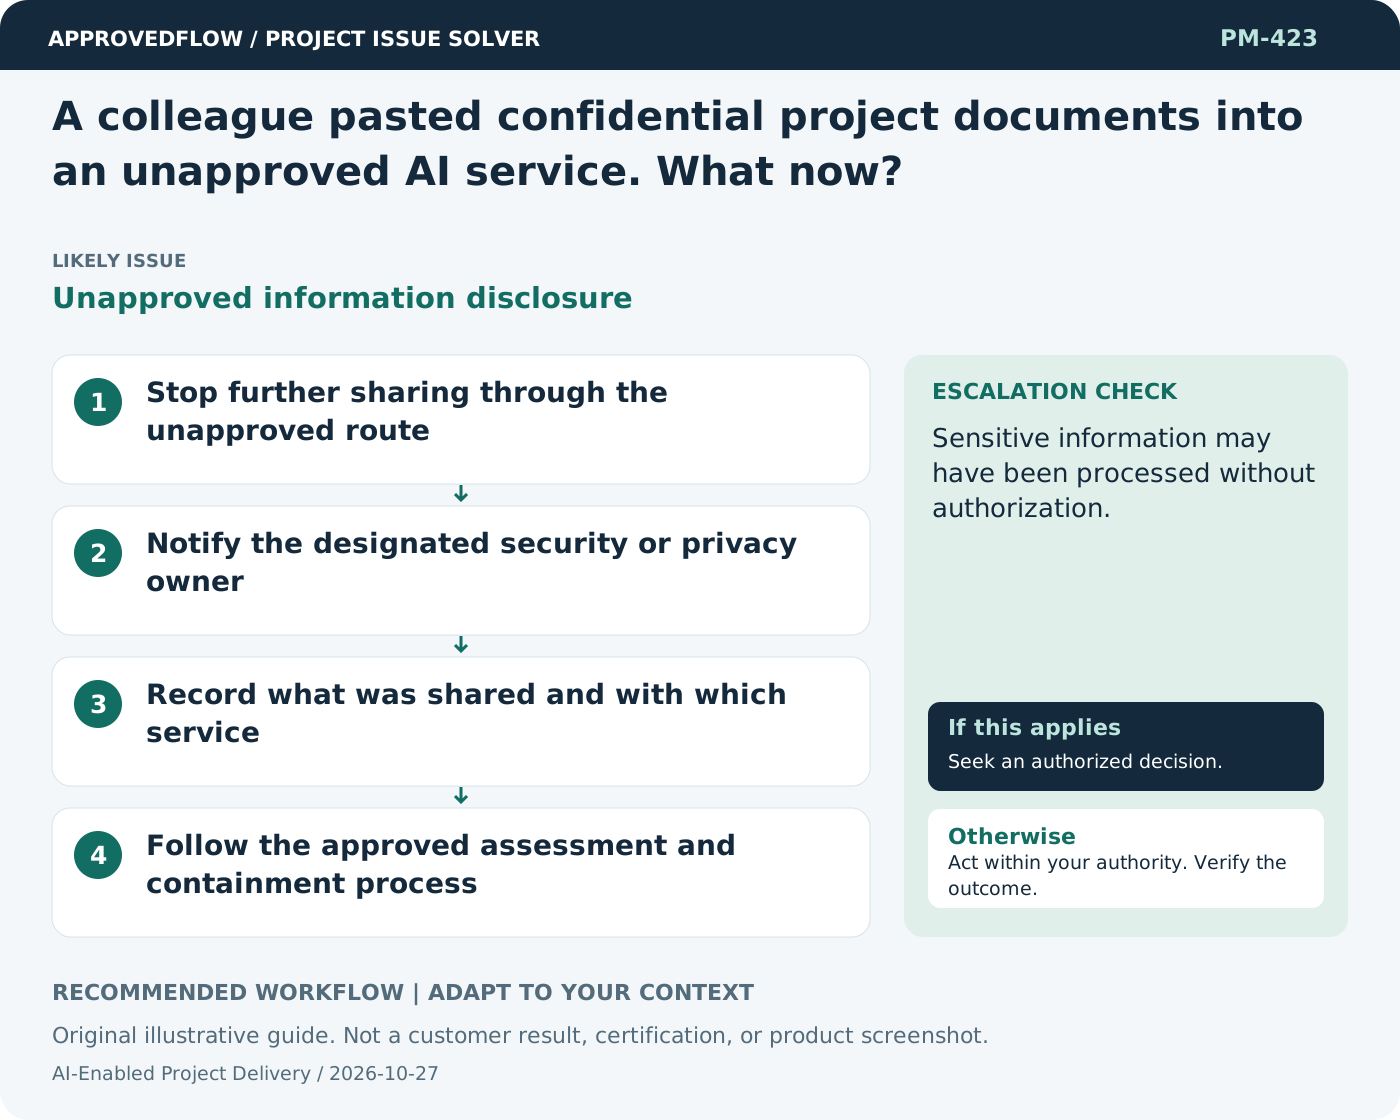
When to escalate
Sensitive information may have been processed without authorization.
The AI service owner and relevant authorized reviewer
Example
A team reports an uploaded supplier contract and moves future analysis to an approved environment.
Mistake to avoid
Uploading the same document to another tool to ask whether the first upload was safe.
Prevent a repeat
Re-evaluate after changes to models, prompts, tools or source data; keep important decisions accountable to people.
Suggested ApprovedFlow setup
- Tasks
- Documents
- Approvals
Track evaluation and review tasks, and keep approved evidence with the work; do not claim the platform provides an unverified AI agent or automated diagnosis. See the platform
Related cases
- The AI search retrieves an obsolete policy. How can we prevent this?Stale knowledge retrieval
- An uploaded document tells our AI to ignore its instructions. What should happen?Untrusted content attempting instruction override
- How do we keep external partners informed without exposing confidential information?Uncontrolled information sharing
- We forgot nonfunctional requirements. What should we check now?Missing service-quality requirements